

Setup checklist
Each item below is a step in this guide.Users and branding
Vendor portfolio
Tag structure
IRQ
Scales
Control sets
Plans and cadence
Templates
Radar
Obligations
Integrations
Step 1: Organization, users, and branding
This step gets your team into the platform and makes everything vendor-facing and stakeholder-facing carry your brand.-
Go to Configuration → Organization, open Members, and choose Invite. Everyone in one batch of invitations gets the same role, so invite in groups:
- Admin has full platform access, including members, roles, integrations and organization settings.
- Member creates and edits vendors, assessments, findings and intake requests across the organization. Most of the risk team starts here.
- Auxiliary Member answers inherent-risk questionnaires, completes tasks assigned to them, and comments on records they are assigned to.
- For a broader rollout, add your email domain under Verified domains on General, so people with that domain can join automatically or request to join. That saves you from creating accounts by hand while you pilot.
- On Branding, set your brand. The Logo is a square icon shown in the app and the vendor portal header. The Full Logo is a wordmark or logotype used in reports and emails. Brand color sets the accent for the vendor portal background. Organizations on the redesigned Organization settings find members under People (choose Invite people) and the brand on General, where the square mark is the Icon and the logotype is the Wordmark.
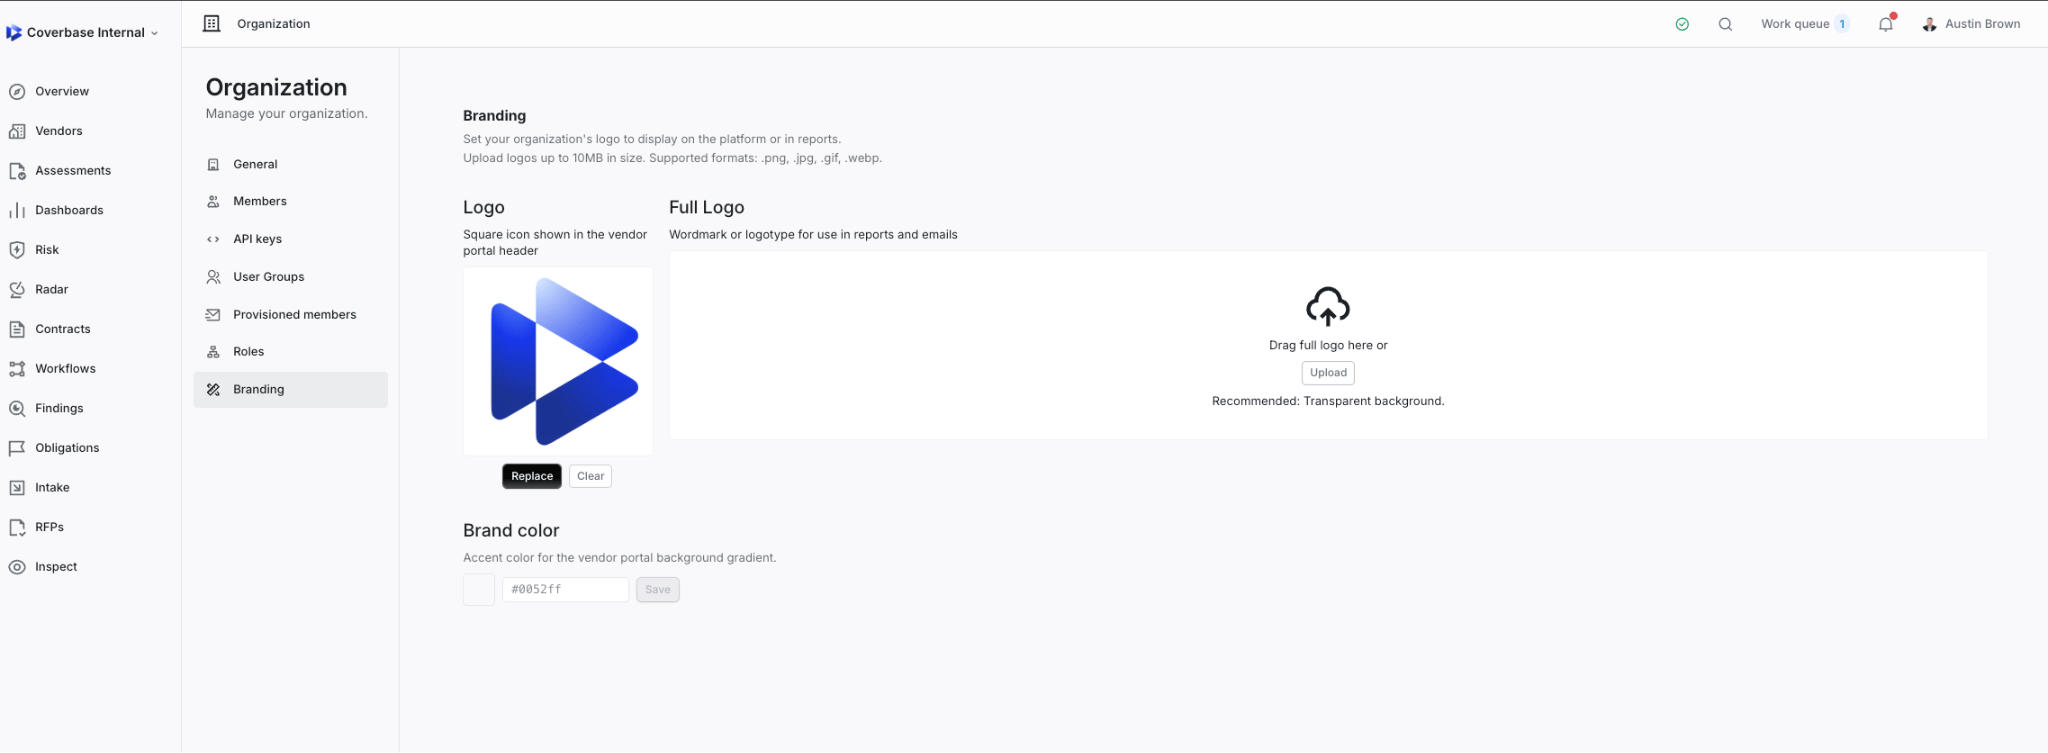
Configuration → Organization → Branding. Your logo and full logo flow into the app, reports, emails, and the vendor portal.
Step 2: Import your vendor portfolio
Loading your existing vendor inventory gives assessments, monitoring, and redundancy checks something to work against. It becomes the library you run reassessments and continuous monitoring from. You need your vendor list with attributes like name, website, description, relationship owner, and contract dates. Your Coverbase contact can hand you the bulk-upload template, along with an enrichment workflow that fills in missing fields.- On the Vendors page, open Actions → Bulk Create Vendors.
- Choose Download template to see the fields, then map your existing data into it. The first sheet (vendor intake) is required and the second (service intake) is optional.
- Upload your file.
- Validate the result. Confirm the vendor count matches your source file, and spot-check a few records to make sure the field values populated correctly.
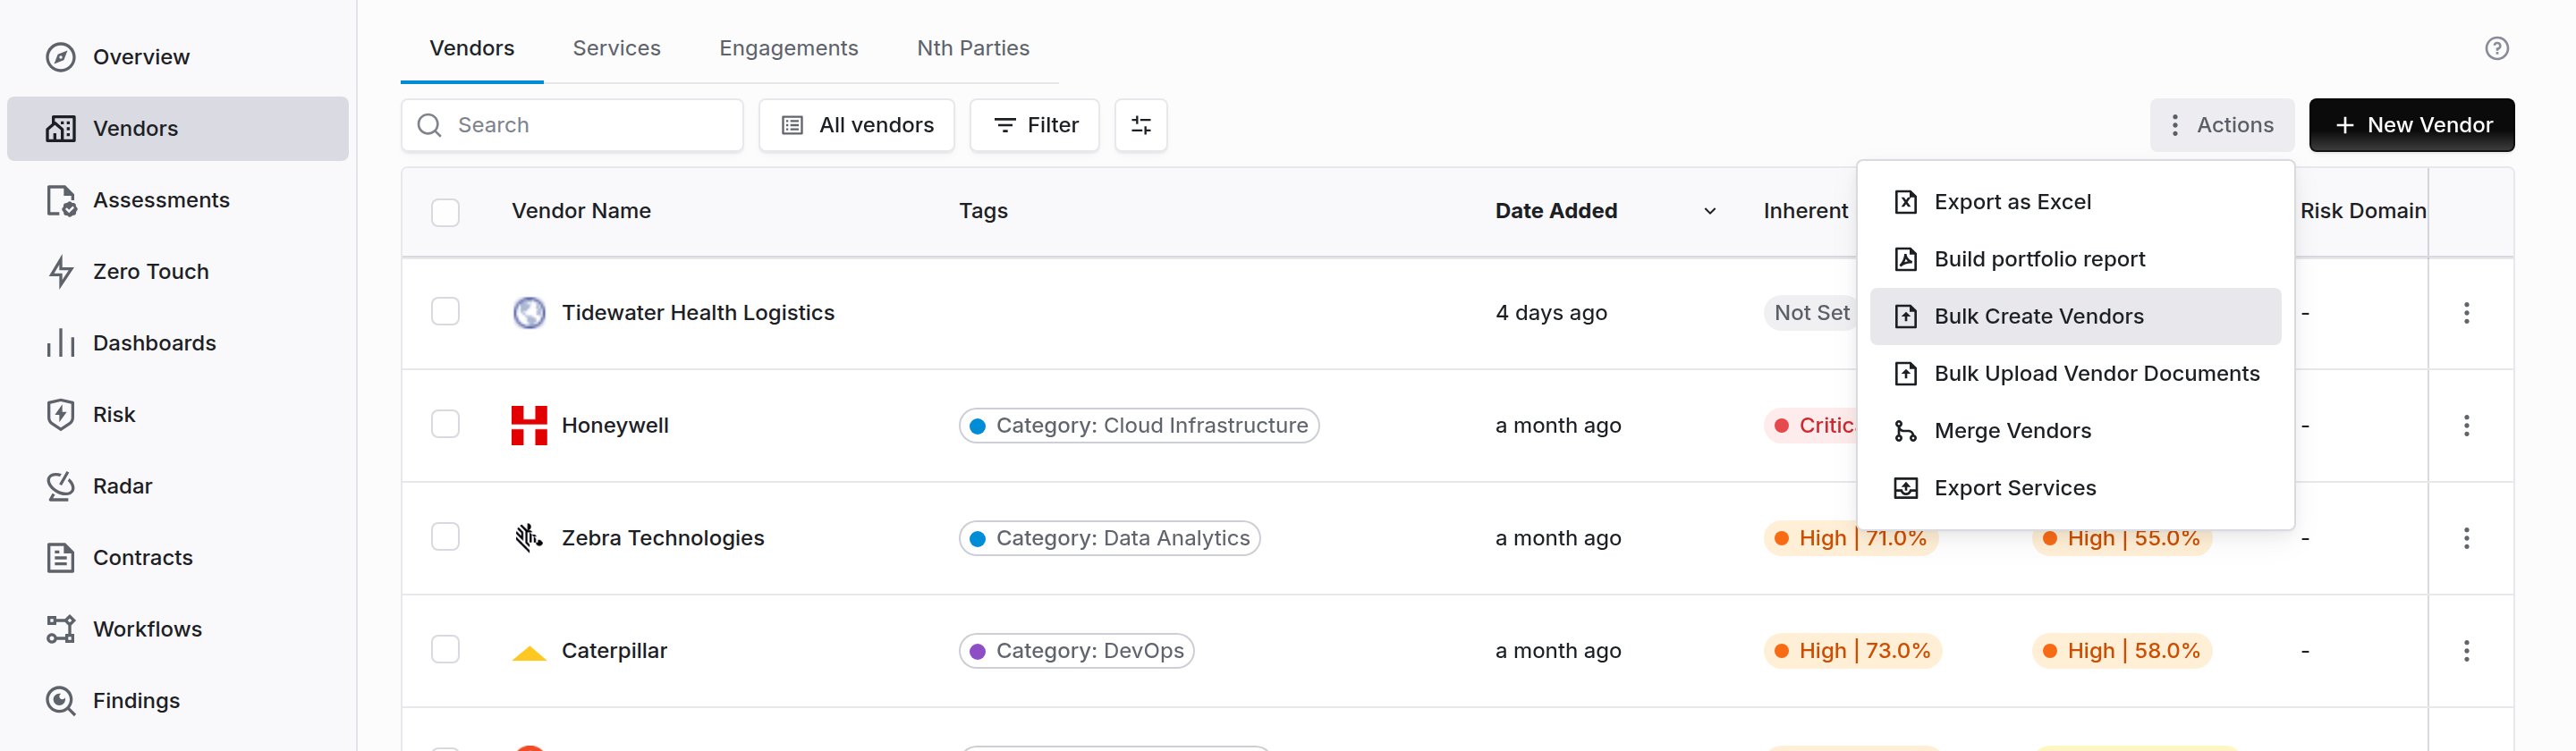
Bulk Create Vendors. Map your existing list into the template and import your whole portfolio at once.
Step 3: Create your tag structure
Tags are the routing layer of the platform. IRQ answers apply tags, and tags then decide which control sets apply, which documents are required, and which due-diligence track a vendor gets. Design the taxonomy before the IRQ, because the IRQ is what fills it in. The structure below works well in practice. Adapt it to your program.Criticality
Data
Access
Geography
Infrastructure
Size and profile
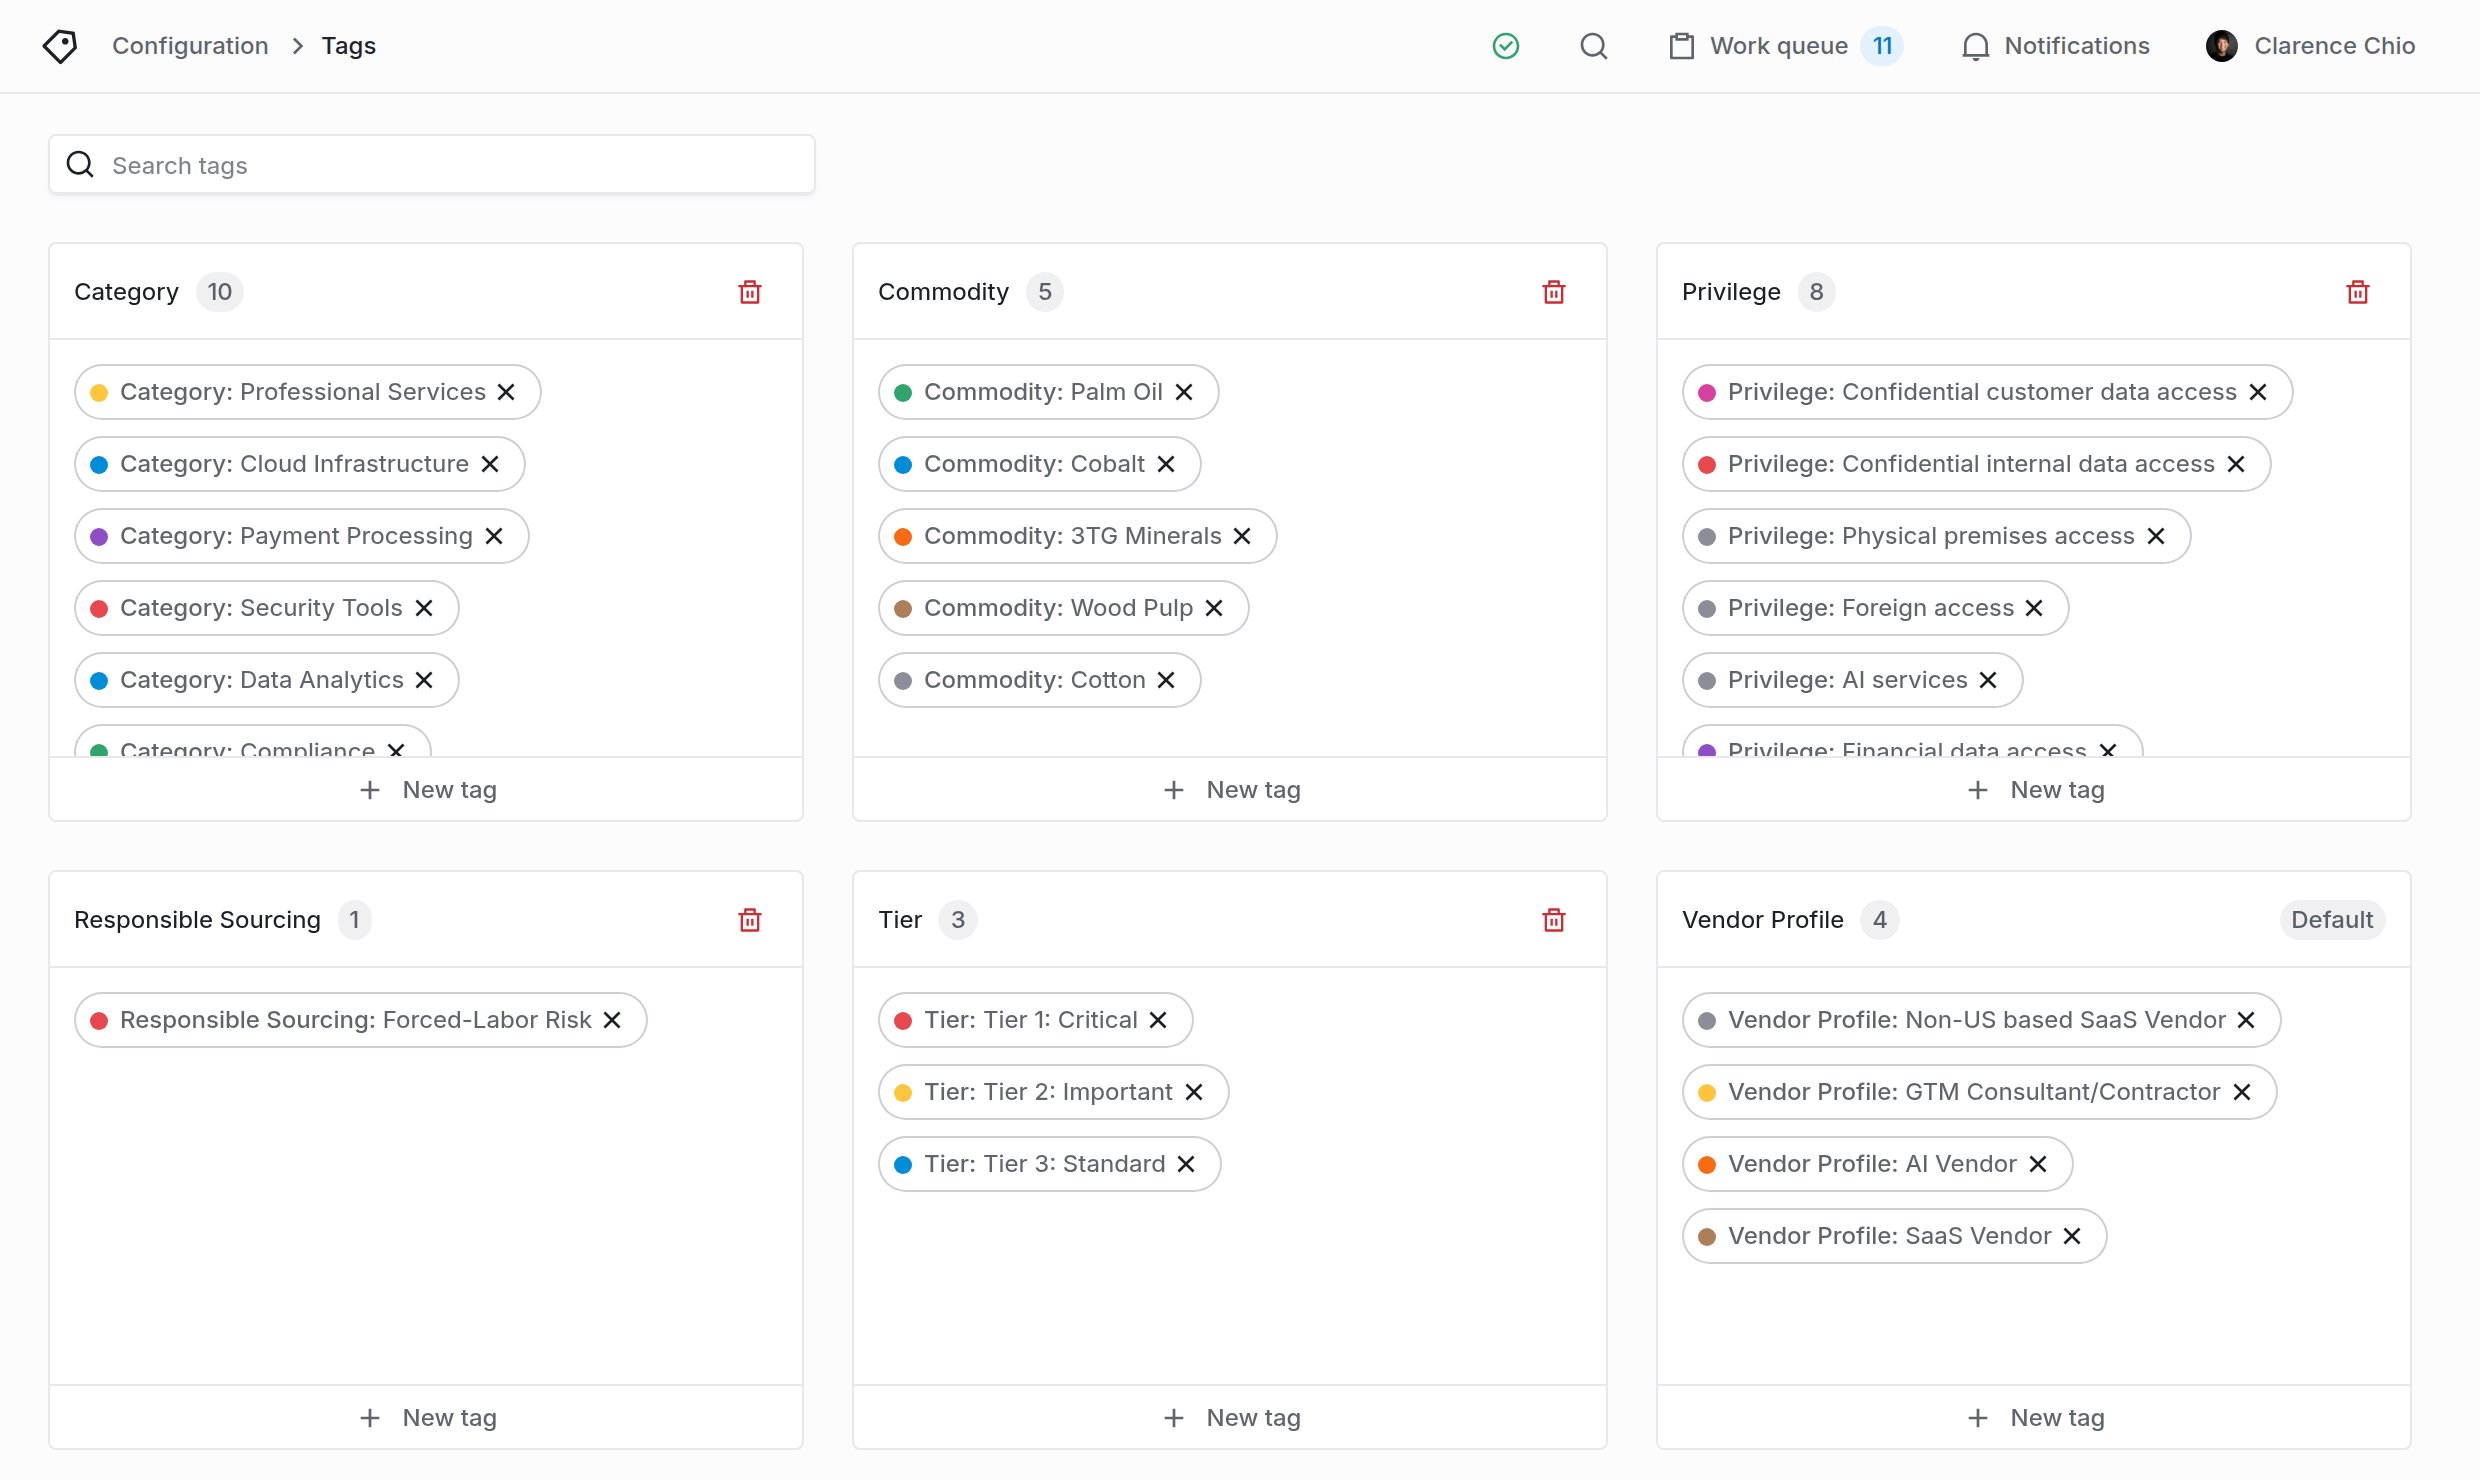
The Tags configuration screen. One card per tag section, and a search box across every tag.
Step 4: Build and weight your IRQ
The inherent risk questionnaire is what business requesters, and Coverbase’s research agent, answer at intake. Its weights produce the inherent risk score, and its response mapping applies your tags. Aim for 15 to 25 concise questions.- Go to Configuration → Questionnaires, stay on the Inherent Risk tab, and choose Create Questionnaire, or start from a packaged template with IRQ Library (see The IRQ library). Use Actions → Bulk Import Questions to import an existing IRQ from a spreadsheet instead of building it question by question.
- Give every answer a Value: its risk weight, where higher means more risk. The sum of all maximum answer values is the risk ceiling, and a vendor’s actual answers as a percentage of that ceiling is their inherent risk score.
- Hover a question and choose Configure write-back to map answers to tags. Data handled outside the US applies “Foreign”, card data applies “PCI”, and so on. Questions built before write-back existed show Configure Response Mapping instead.
- Add conditional logic where a follow-on question should only appear based on a prior answer, like asking for data-flow details only if data is exchanged.
- Set per-question AI guidance to control what the research agent may use when it auto-answers. For example, “only source from the vendor’s trust center, exclude blogs and CVE chatter.”
- Mark judgment questions as Required so the AI never auto-answers them without human input.
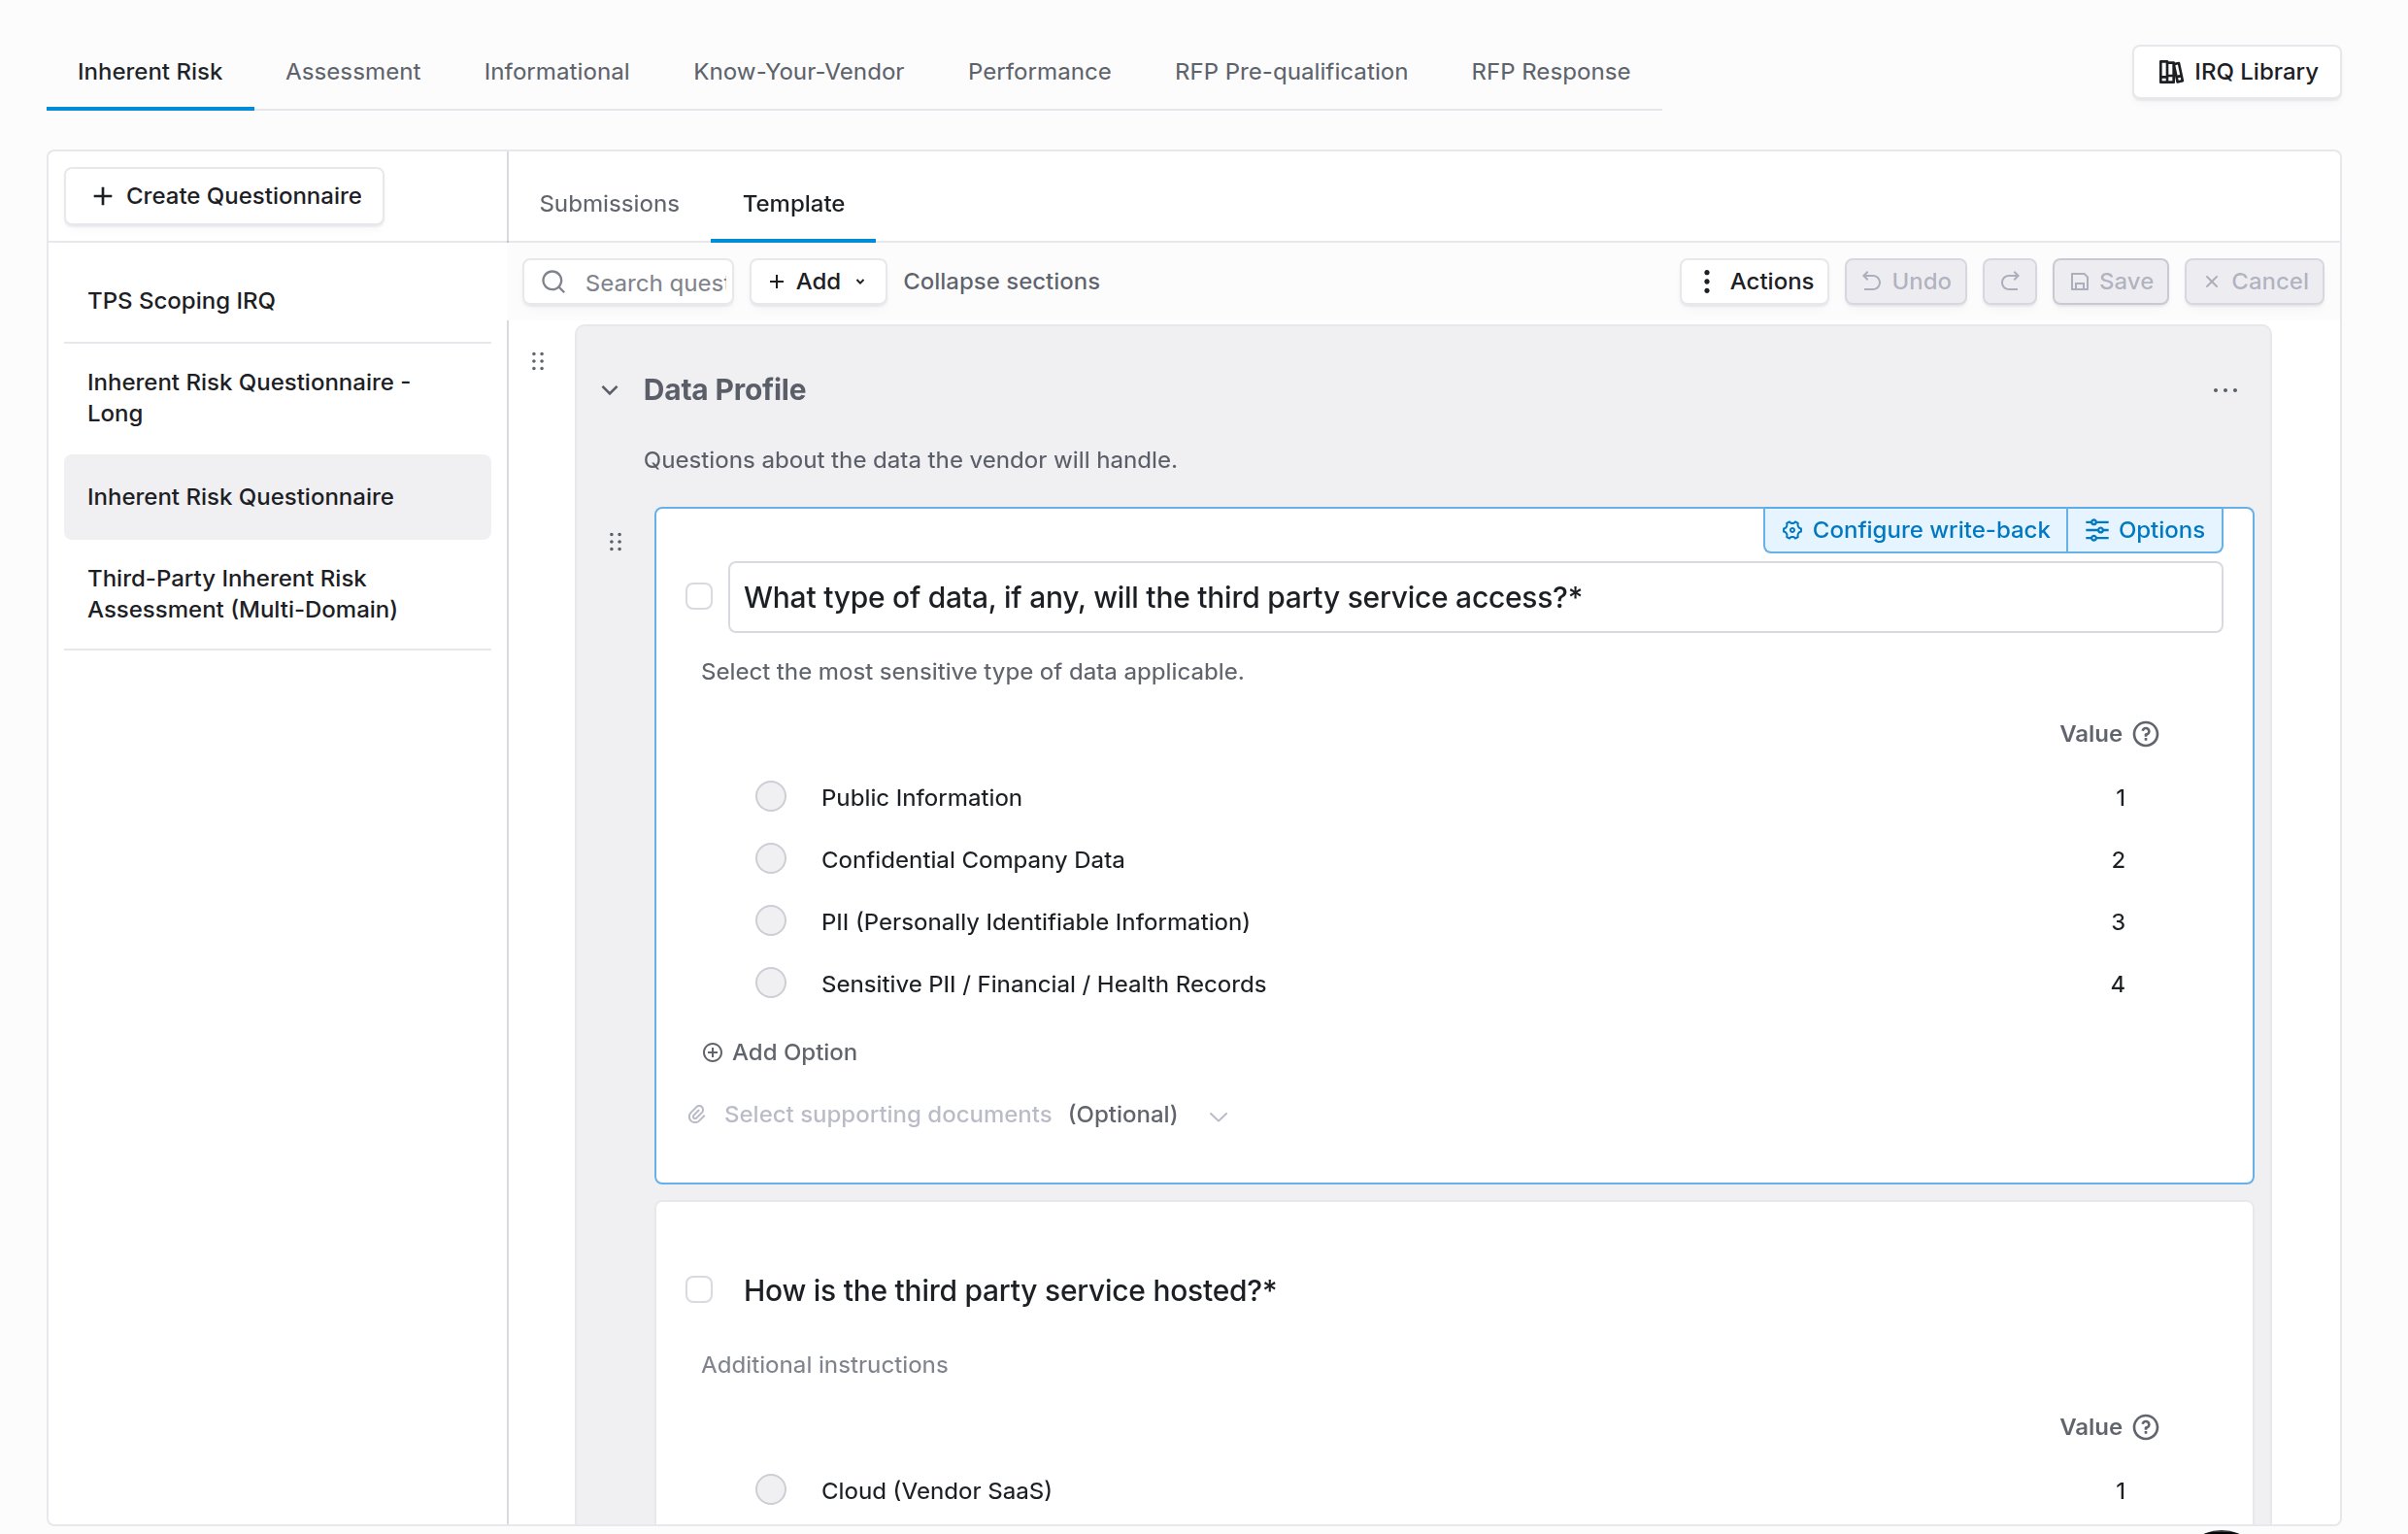
The IRQ builder. Each answer carries a value (right column), and Configure write-back links answers to the tags that route the vendor.
Example: mapping answers to tags
The mapping is what powers automated routing. When someone answers “This vendor will process employee data,” Coverbase applies the Employee Data tag, which then triggers specific control sets and document requests.Pattern: auto-escalating vendors to Critical
A common requirement is that if a vendor answers “yes” to two or three specific questions, they should land in the strictest track regardless of overall score. Use these mechanisms together for redundancy:- Set a Score override on those answers (the menu beside the option). While the answer is selected, the questionnaire’s overall score cannot fall below the percentage you enter, so a single “yes” can hold the vendor in your critical band.
- Weight those questions heavily, so any “yes” pushes the score up on its own.
- Map those answers to a tag that routes the vendor to the stricter due-diligence track, with control sets and document requirements keyed to that tag.
Step 5: Configure risk and compliance scales
Scales define the bands your program scores against. There are two: the vendor-level risk scale and the per-control compliance scale.- Go to Configuration → Scoring and open the Risk Scoring tab. The default bands are 0 to 25 low, 25 to 50 medium, 50 to 75 high, and 75 to 100 critical. Every threshold is adjustable, and you can add or remove tiers, collapse to three, or lower the critical threshold.
- On the Control Scoring tab, review the compliance scale used on controls. The default runs from 4 (fully compliant) down to 1 (not compliant). You can rename levels, add or remove them, or make it boolean.
- Write criteria into each level, not only labels. The criteria text is used when scores are assigned, so “one or more failing conditions met” is more useful than a bare “low.”
- Add custom assessment scales with New Scale on the Control Scoring tab if your program rates other dimensions, like RFP alignment, ESG alignment, or contractual protection.
- Under Risk Display on the Risk Scoring tab, choose whether residual risk is shown at all (Track residual risk) and whether numeric scores appear next to risk levels (Display numerical scores). Scores are still calculated and stored either way.
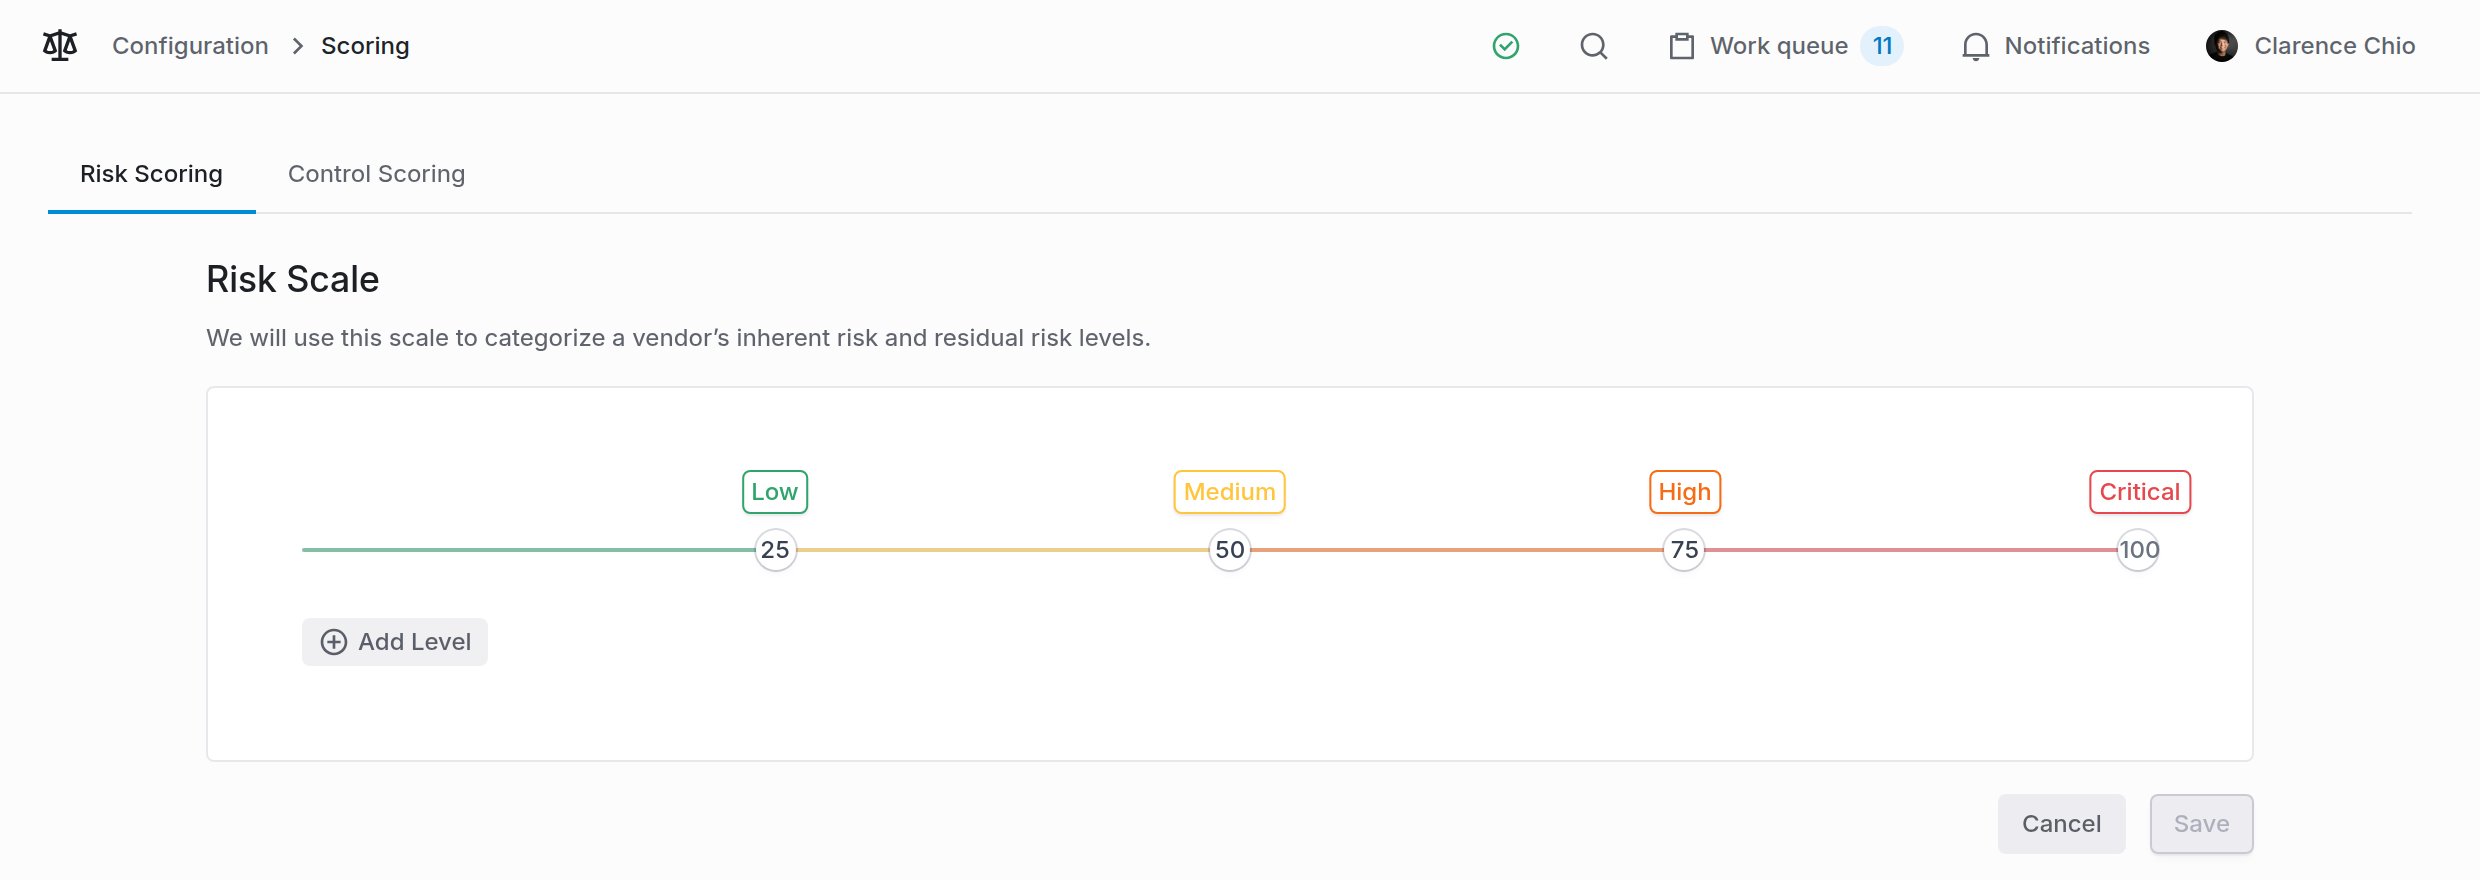
The risk scale on the Risk Scoring tab. Adjustable bands from low through critical.
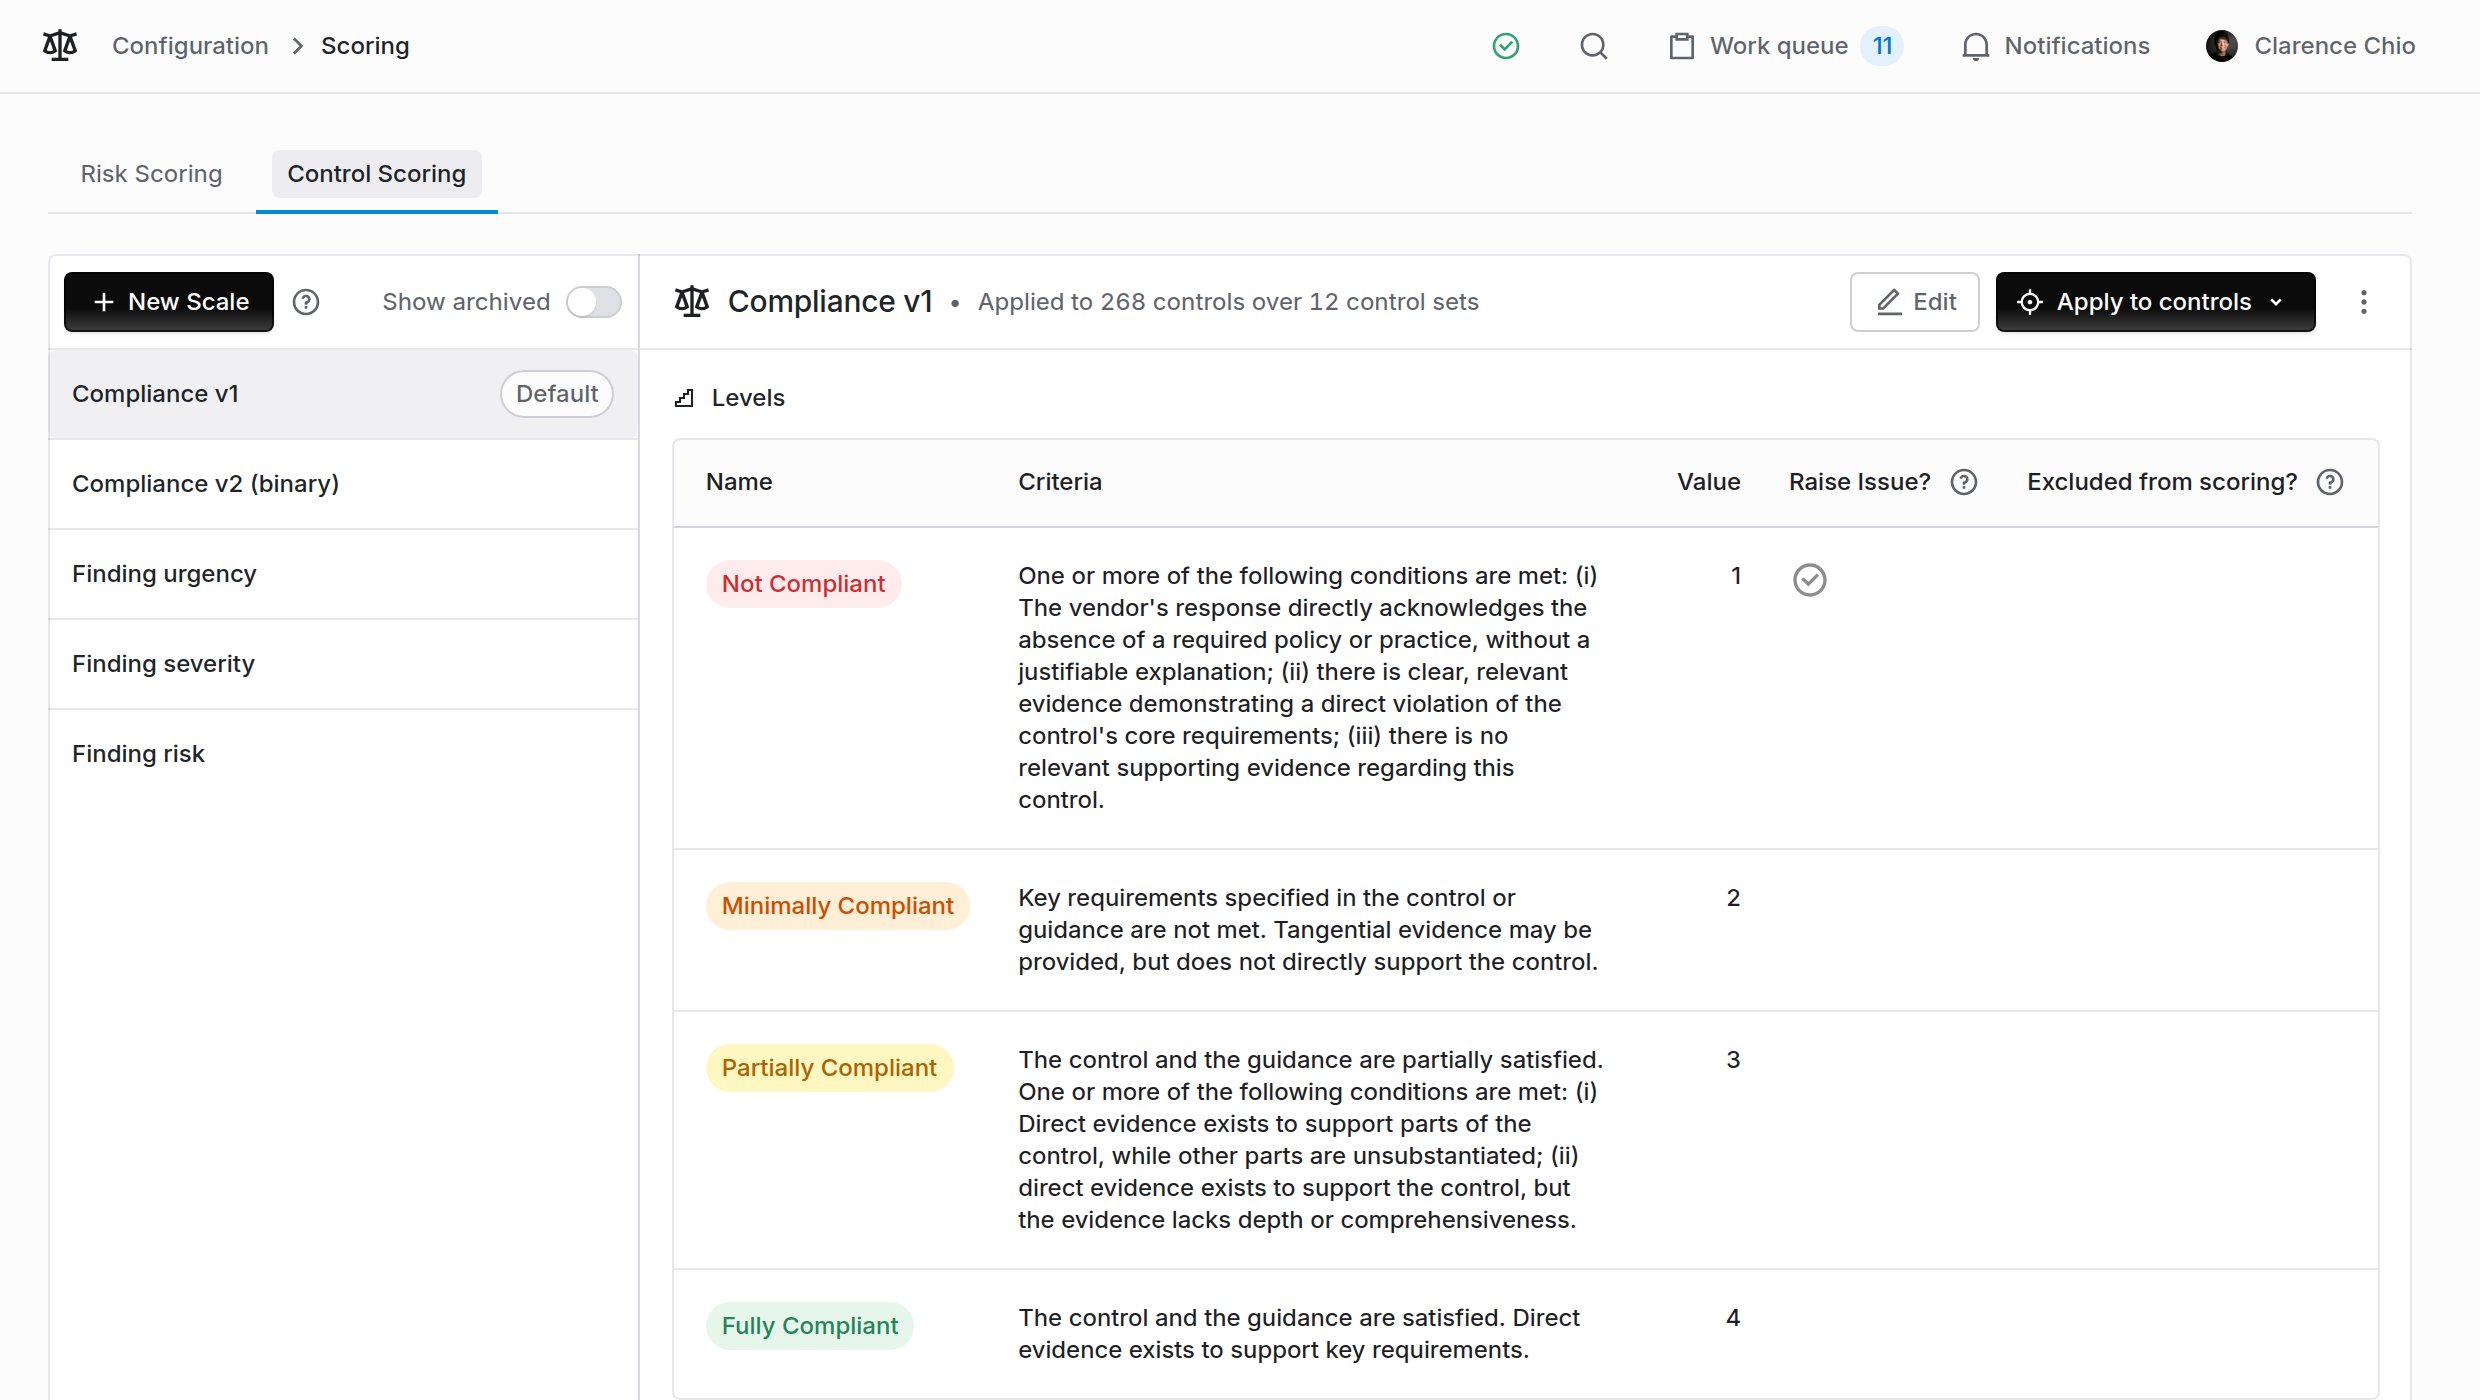
The compliance scale on the Control Scoring tab, used on individual controls. Rename, add, remove, or make it boolean.
Common custom scales beyond compliance
Common custom scales beyond compliance
- RFP alignment: Exceeds, Meets, Partially meets, Does not meet requirements
- ESG alignment: Strong, Developing, Limited, No ESG program
- Contractual protection: Strong (indemnification, insurance, SLAs), Standard, Limited, Inadequate
Decide whether service scores set the vendor’s score
A service-scoped assessment scores the services it covers. By default it leaves the vendor’s own score alone, so a vendor can read medium while one of its services reads high. Risk Roll-up changes that. It sits under Configuration → Scoring on the Risk Scoring tab, below the risk scale. There is one switch per risk type:- Roll up inherent risk from services
- Roll up residual risk from services
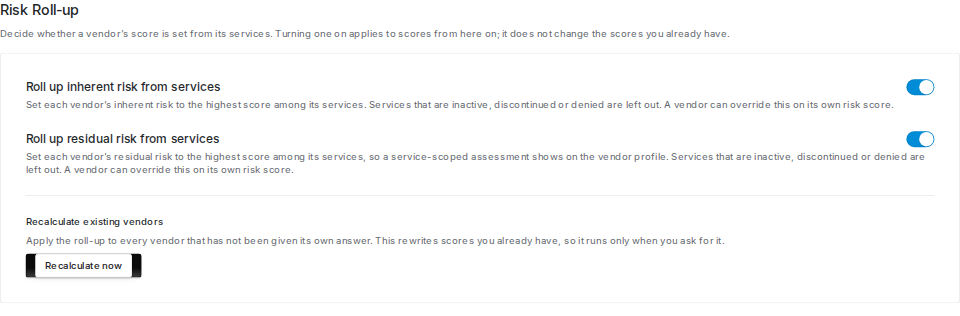
Risk Roll-up on the Risk Scoring tab. One switch per risk type, and a separate action for the vendors you already have.
Step 6: Upload and tune control sets
Control sets are what assessments measure against. They define what “good” looks like. Coverbase ships with SIG, NIST (CSF and AI RMF), ISO 27001, NYDFS, FFIEC, PCI DSS, DORA, and more out of the box, and your own frameworks import from a spreadsheet. If you buy physical goods rather than software, look under Operations & Supply Chain in the Vendor Controls Library. Those templates ask a supplier whether it can keep your production line fed (continuity testing, alternate sourcing, batch traceability, chain of custody, restricted substances) rather than how it secures a network. The Control Set library lists all of them.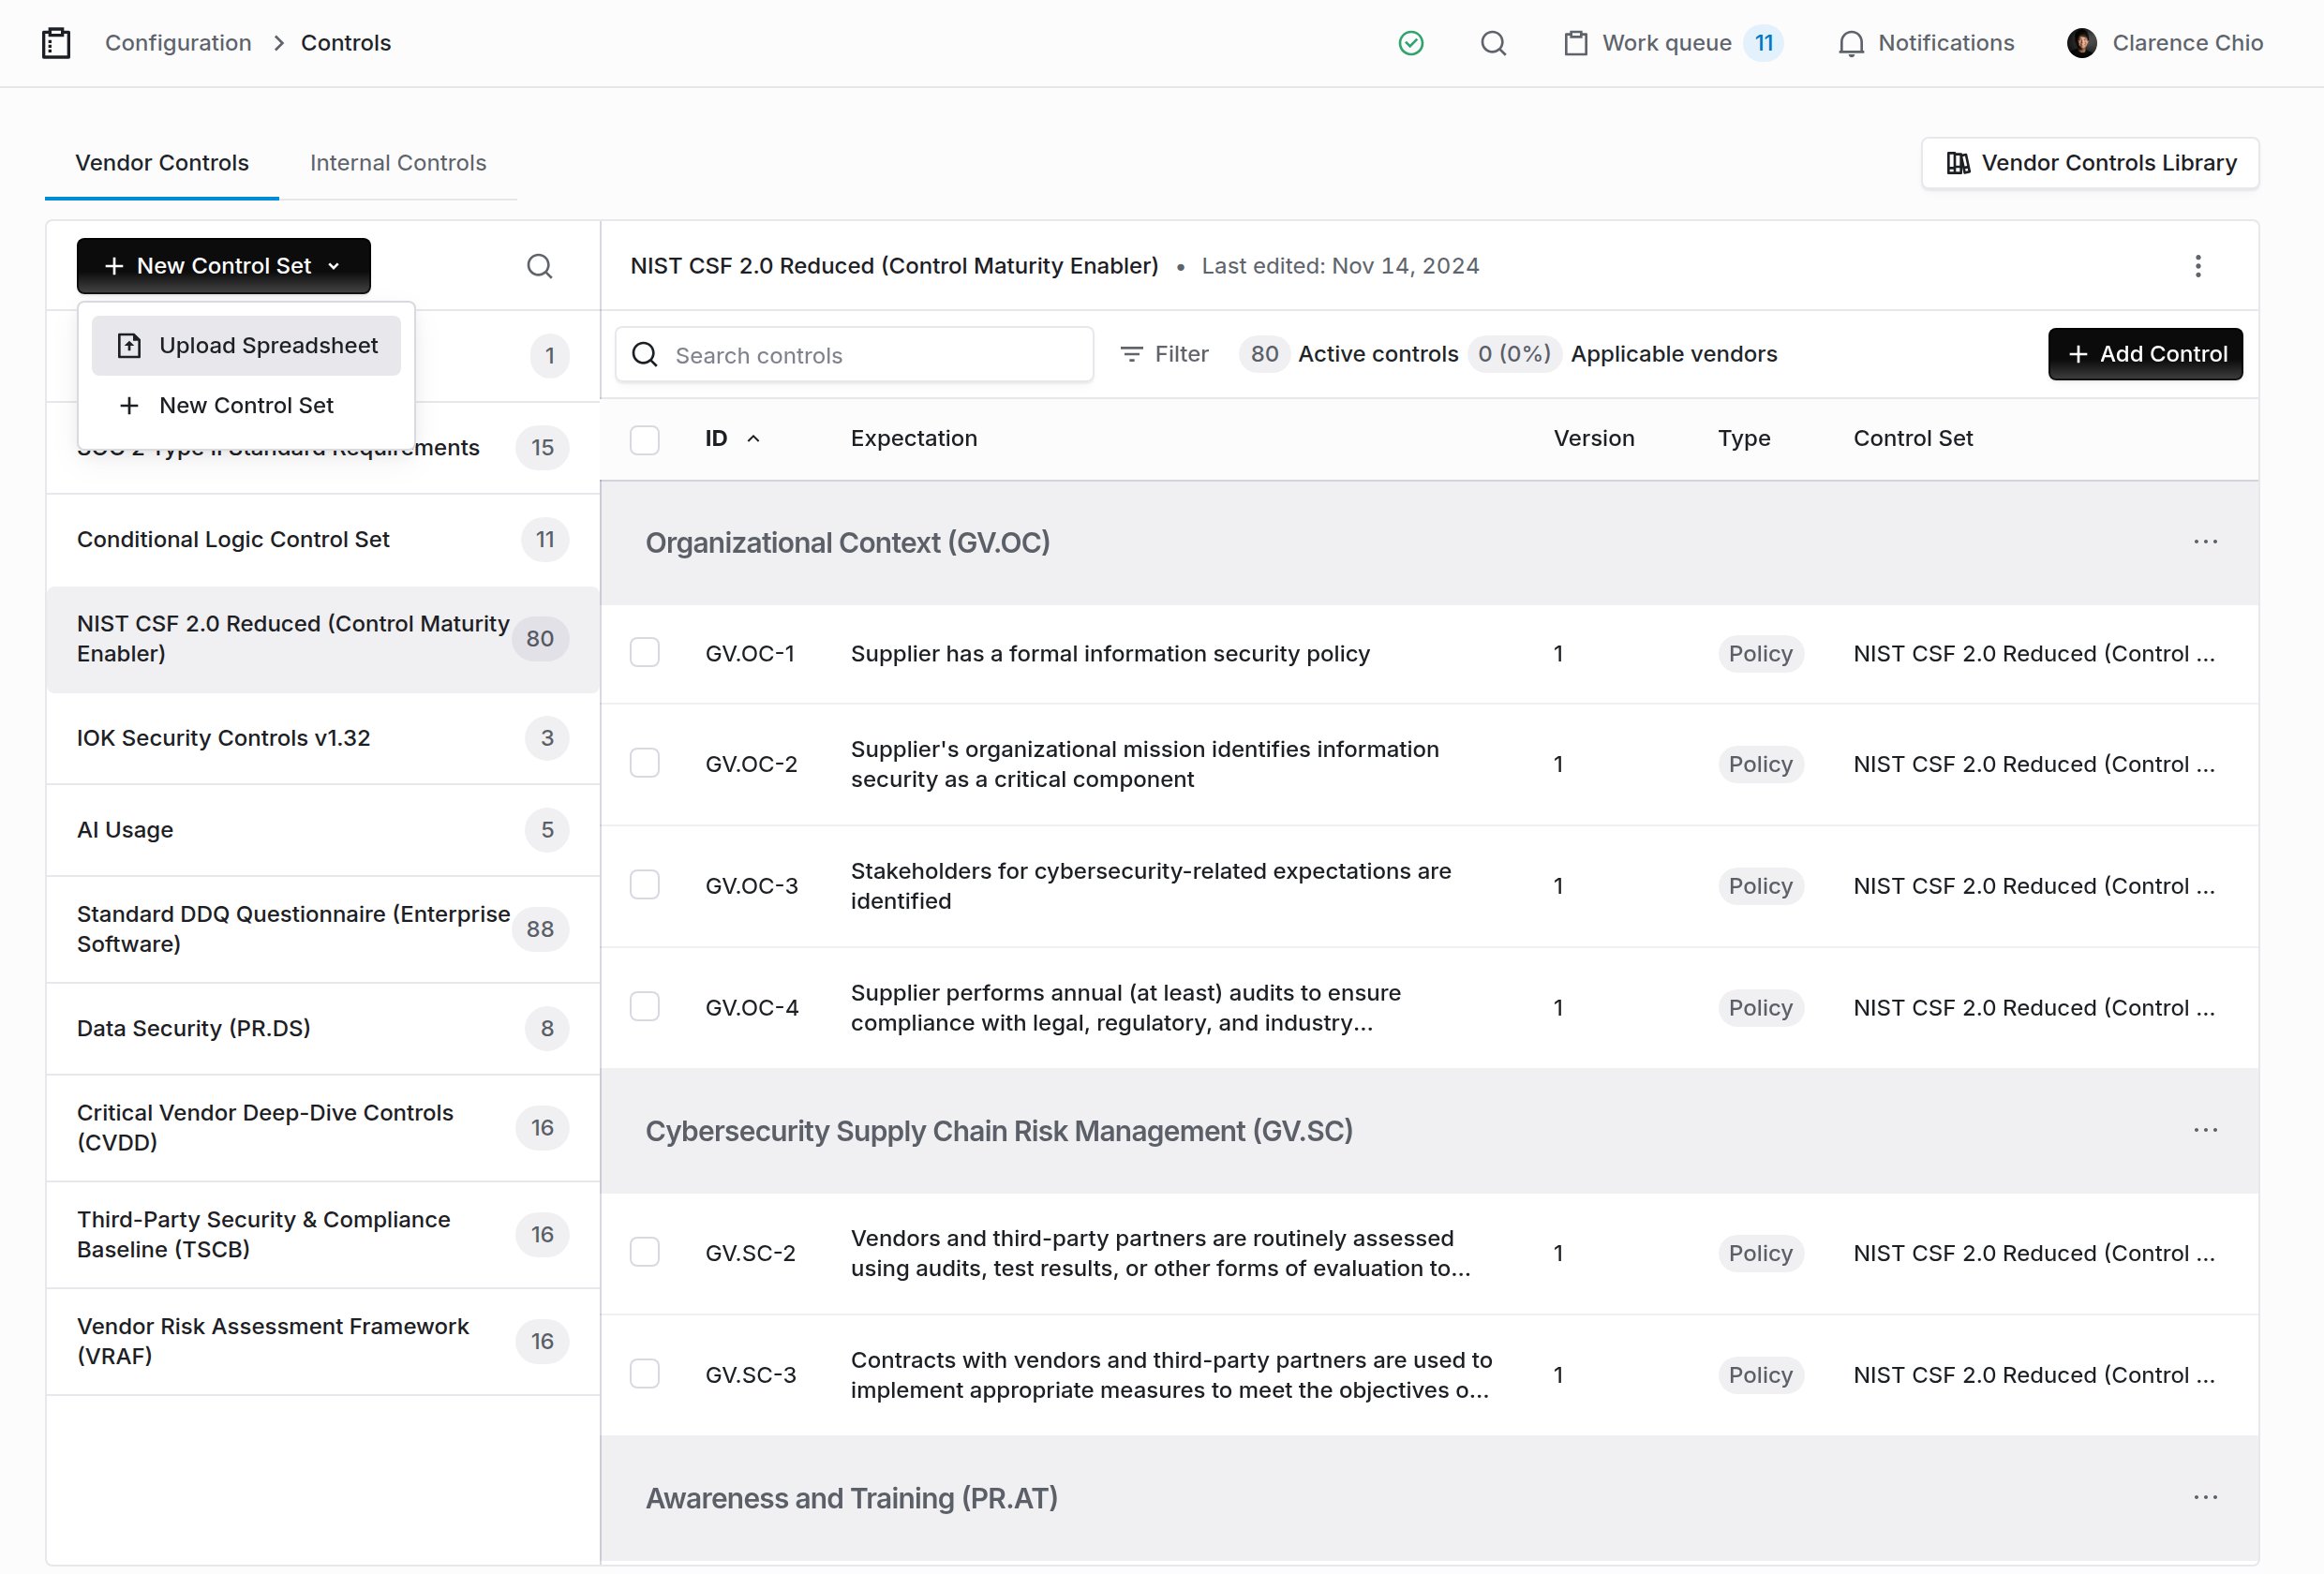
The Controls page. Your control sets on the left, each with its controls, versions, and applicable vendors. Vendor Controls Library opens the packaged frameworks, and New Control Set offers Upload Spreadsheet.
Importing your own controls
- Go to Configuration → Controls and click New Control Set → Upload Spreadsheet. Download the template workbook and the tips document from that dialog, which always holds the current version. In the workbook, the Controls tab is the one that gets imported; the Instructions tab carries the tips, and the Document Types and Risk Domains tabs are there for reference.
- Use an LLM to convert your existing framework (from your GRC tool, a spreadsheet, wherever it lives) into the template format. Paste your controls plus the tips doc and ask for the conversion.
- Upload one control set at a time and verify the import. Start with your two or three most critical frameworks.
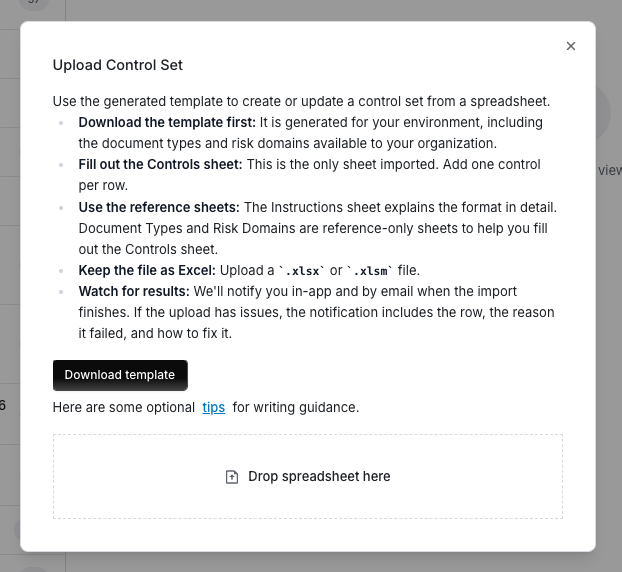
The Upload Control Set dialog. Download the template first, fill in the Controls sheet, and drop the file back here. The tips link opens the writing guidance.
Per-set configuration
Every control has three parts: the expectation (what you are measuring), the question (how it would be asked of a vendor if evidence is missing), and the guidance (how the AI should evaluate it). Then, per set:- Applicability: map which tags and inherent-risk levels this set applies to. This is what makes assessment assignment automatic.
- Risk domains: assign controls to domains like InfoSec, compliance, or operational resilience, so review work can later be split across specialists.
- Strictness: set the evaluation toggle (lenient, standard, or strict) per set.
- Evidence sources: choose what the AI may draw on per control, from specific document types to web search to a vendor’s Vendor Intelligence. These combine and can be prioritized, so you might put the information security policy first and web search as a fallback.
- Minimum credibility: on each web-search source, set how accountable a publisher has to be before its page can be cited: No minimum, Reputable (the default), or Authoritative. Pages below the bar are discarded before the AI reads them. See Evidence quality and source credibility for the scale, where to tighten it, and what it does not cover.
- Restrict evidence to these sources: on by default once you add evidence sources at the set level, this keeps the analysis inside the sources you listed. Turn it off when you want to ask the vendor for particular document types without narrowing what the AI may read. The sources still drive the portal request and stay the AI’s first stop, but other submitted documents remain admissible. Evidence sources set on an individual control always restrict that control.
- Document requirements: mark documents required or suggested. Required blocks portal submission until the document is uploaded, so use it sparingly.
A document-requirements pattern that works
A document-requirements pattern that works
Per-control tuning
Open any control to edit its expectation, weight, and guidance. Guidance is where conditional logic and exceptions live, like “mark fully compliant if the vendor is not a professional services company with a physical on-site presence,” or “accept an infosec training attestation as sufficient evidence.”Step 7: Assessment plans and reassessment cadence
This step decides which assessment a vendor gets, and when they get looked at again.- Build assessment plans that bundle control sets by tier, so high and critical vendors get the fuller plan. Plans can be assigned statically or dynamically off tags and inherent risk.
- Set the reassessment cadence under Periodic Re-assessment Settings in Configuration → Assessment Settings. The Timeline sets how many days before the reassessment date stakeholder reminders go out, document collection starts, and the assessment should be ready for review. Each Reassessment rule names an assessment plan, the risk levels it covers, and the Months between reassessments. Rules match suppliers on inherent risk level by default; set Match suppliers on to residual risk level to key off residual instead (a supplier with no residual level yet falls back to inherent). A vendor’s next reassessment date can still be changed by hand.
- Layer on trigger-based reassessments so a Radar event or a risk-score change can open an off-cycle review automatically.
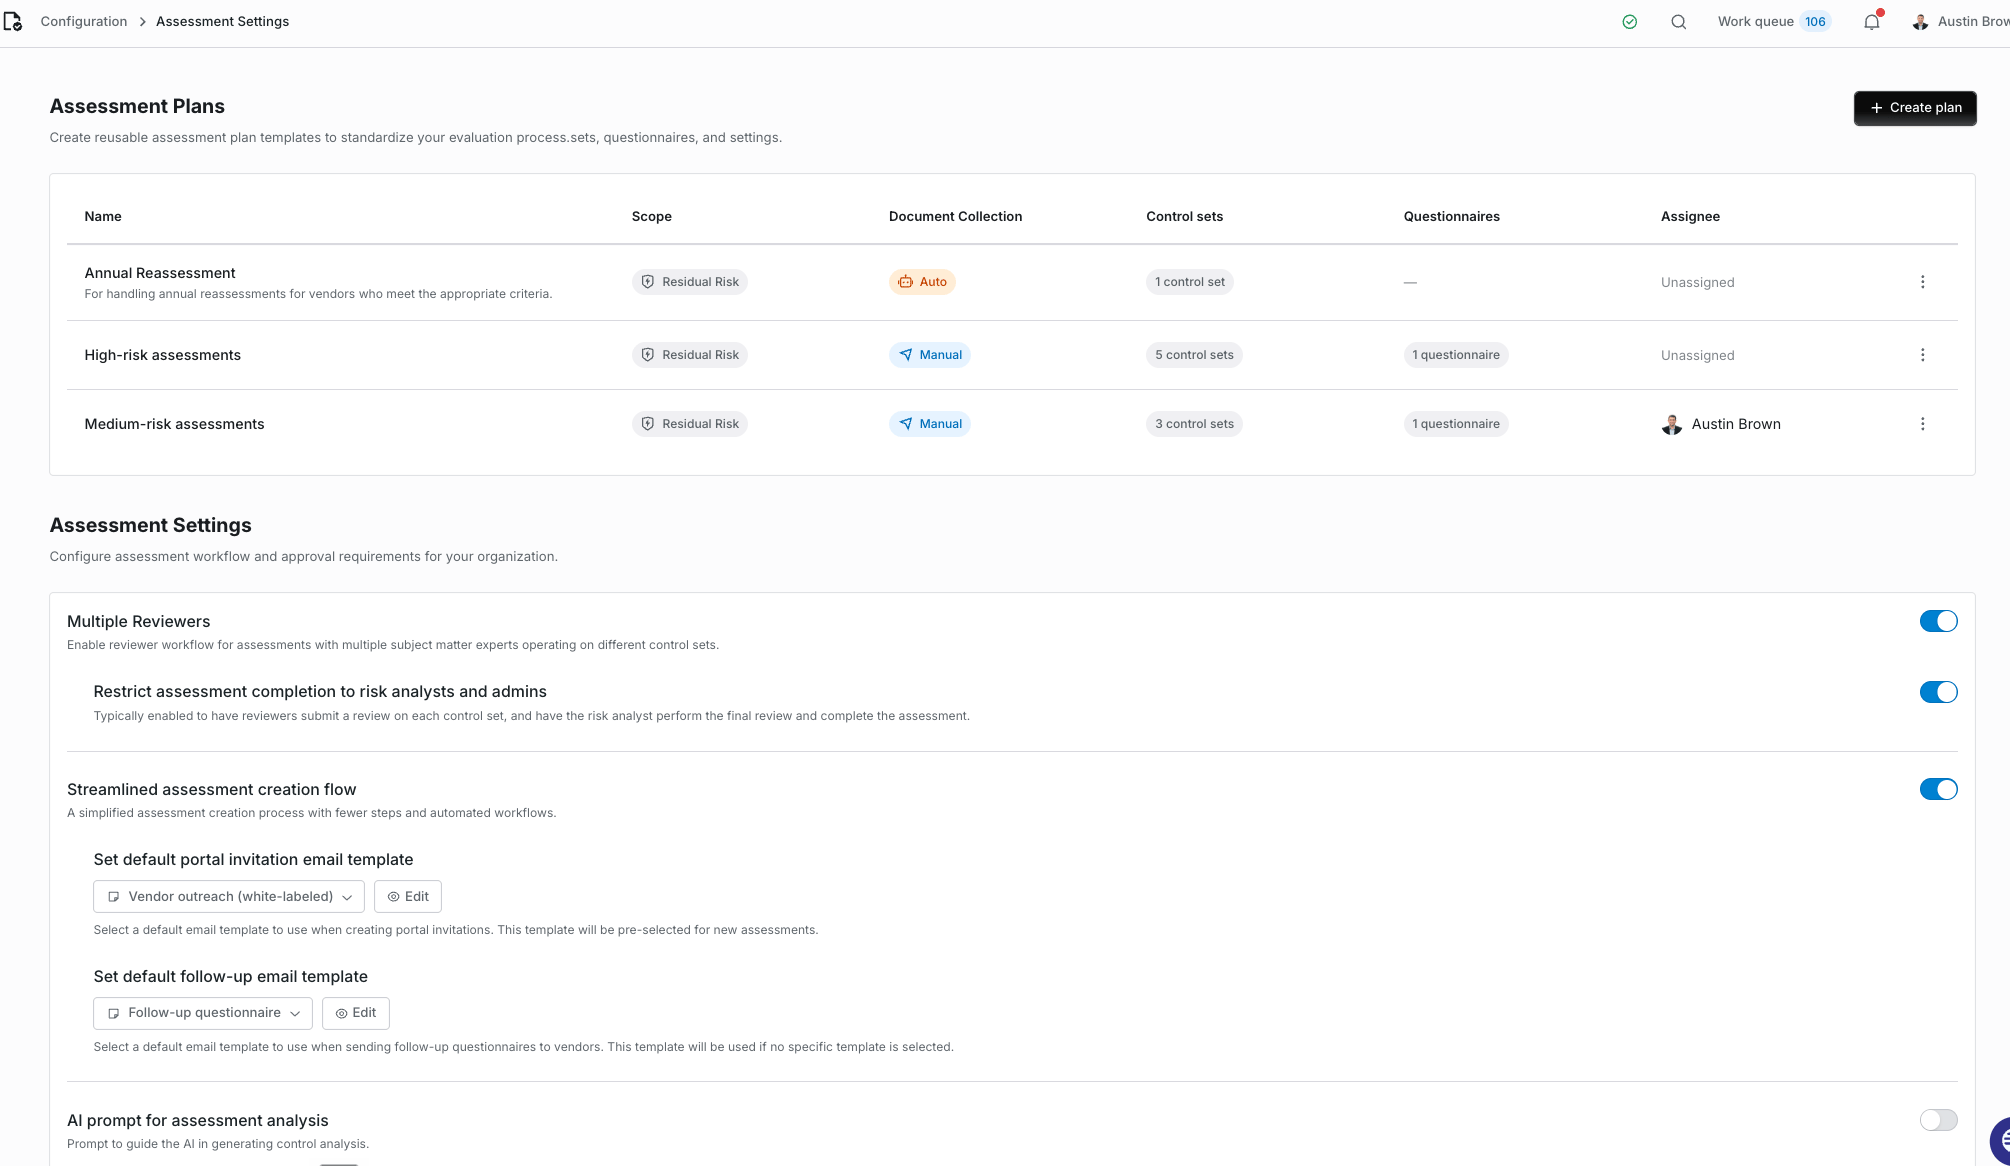
Assessment plans on Configuration → Assessment Settings. Each plan bundles control sets and questionnaires with its scope, collection mode and assignee.
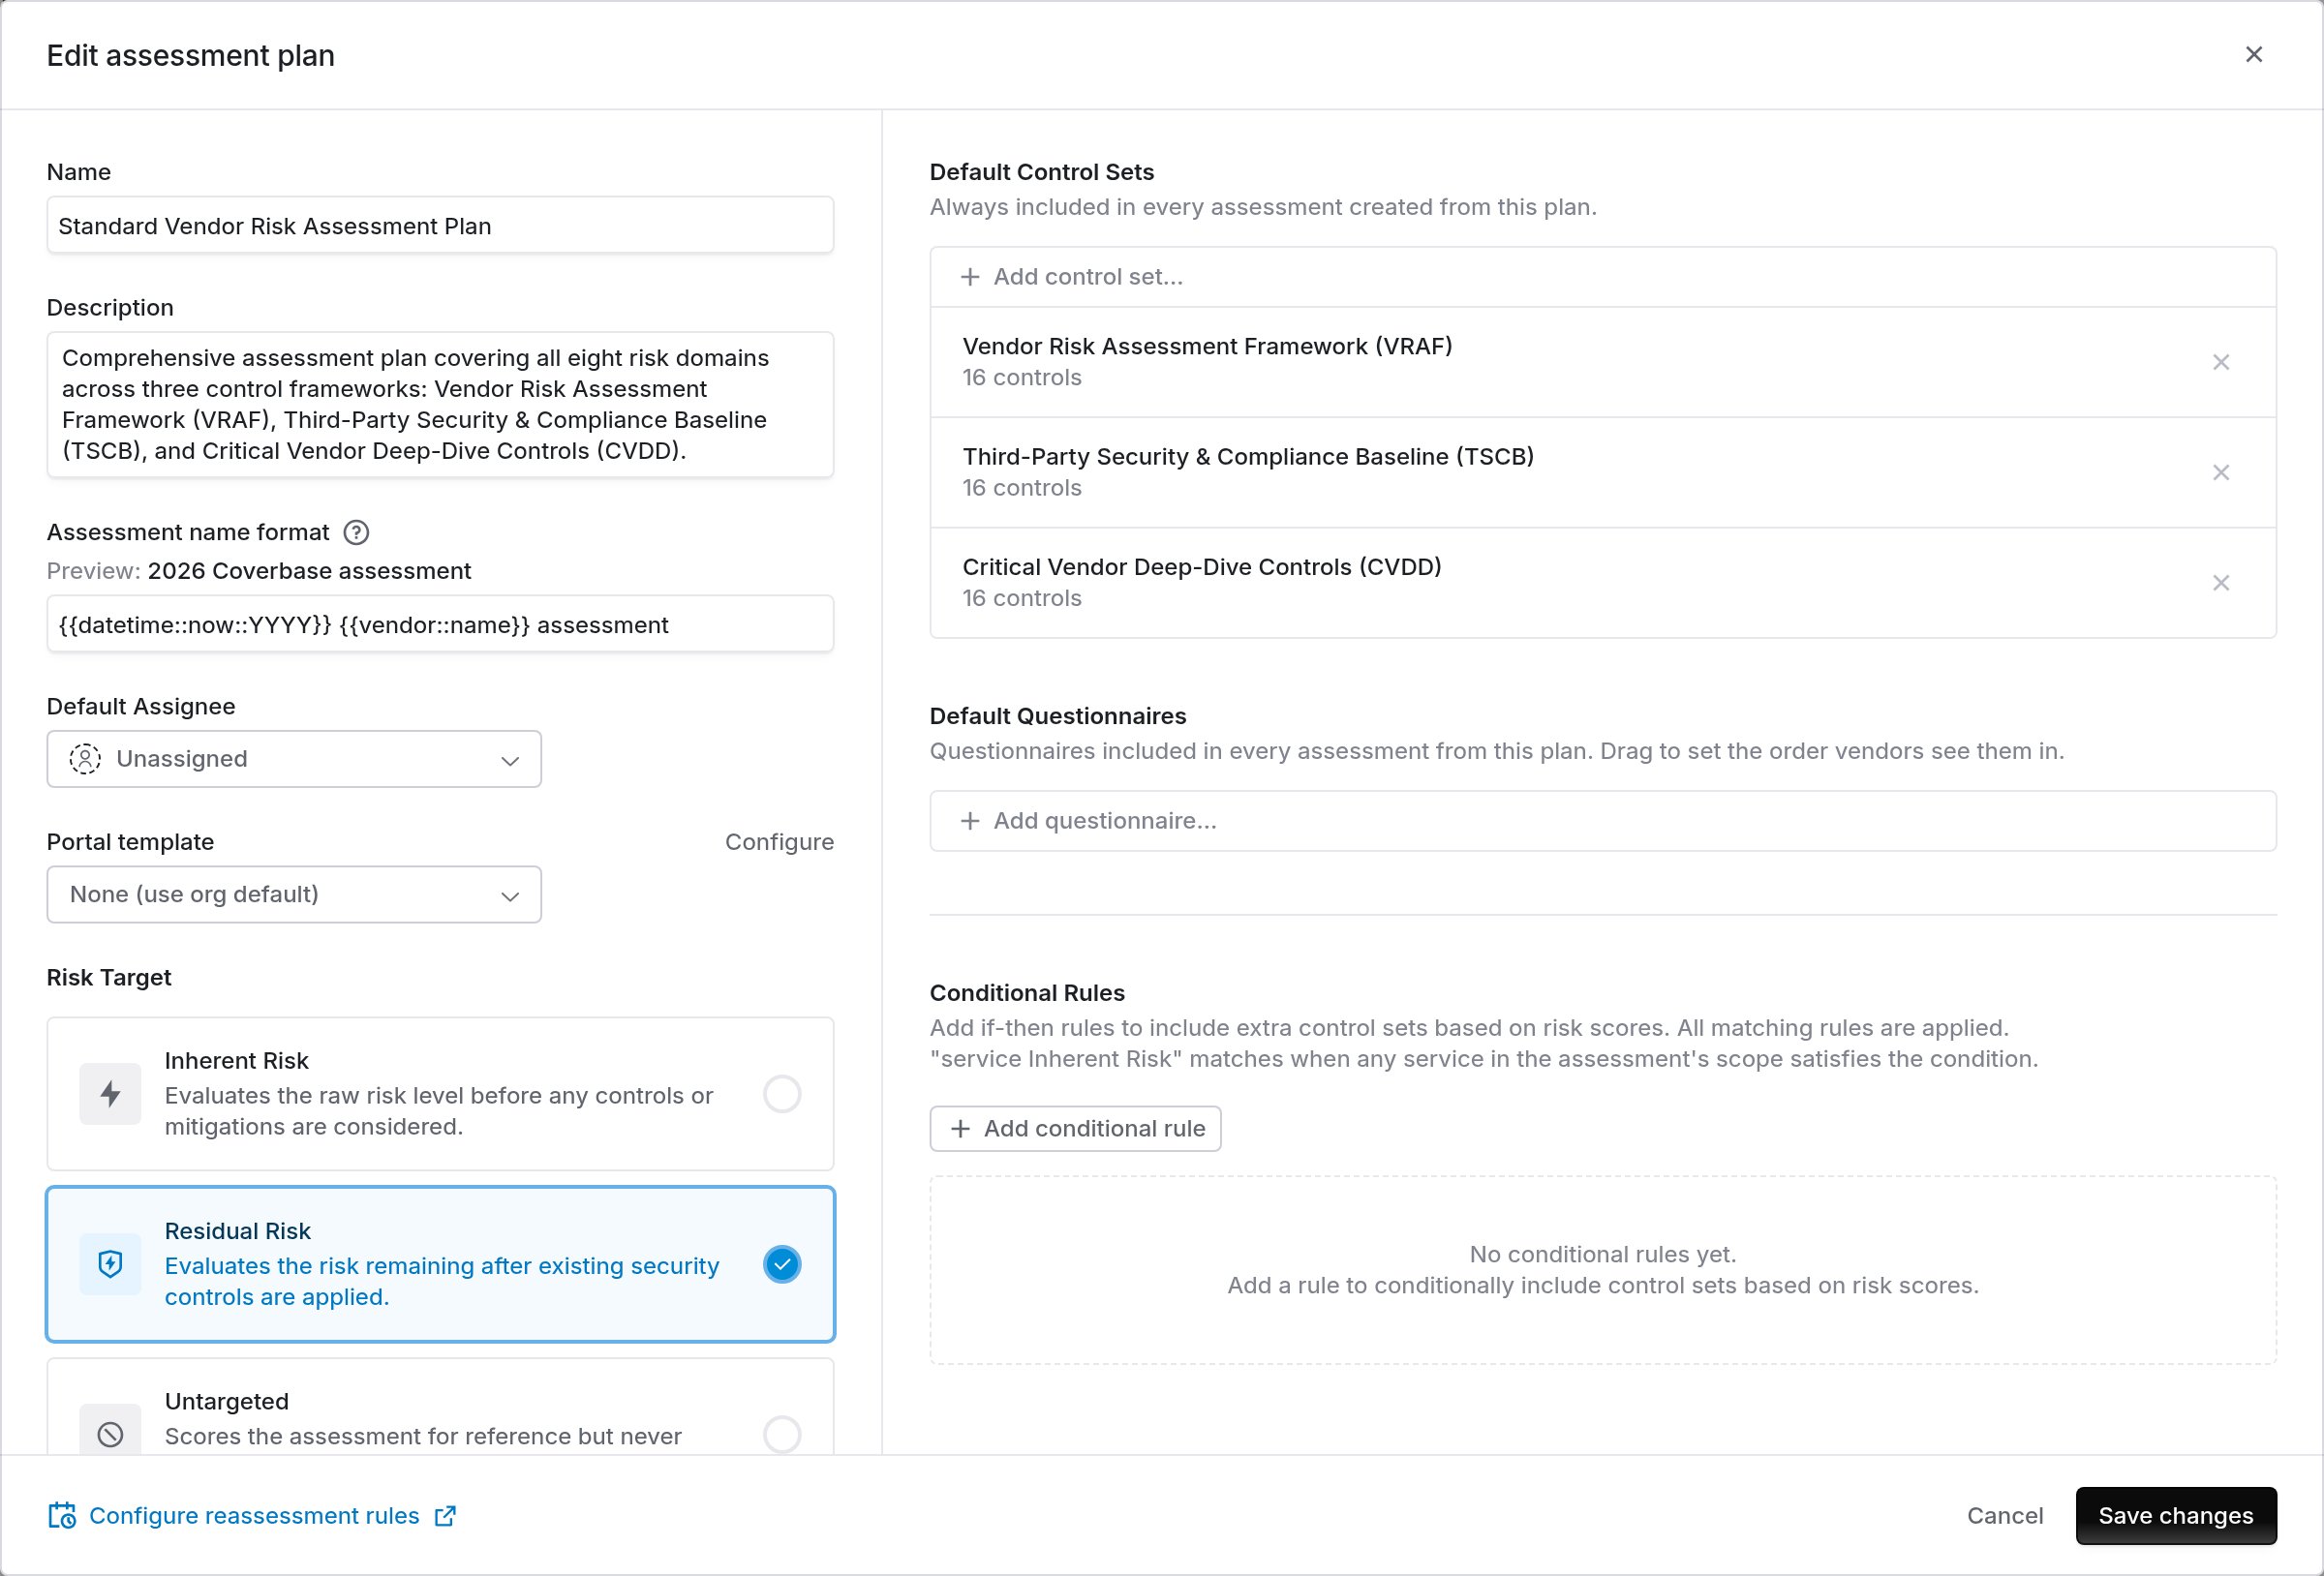
Editing an assessment plan. Default control sets and questionnaires, conditional rules that add control sets by risk score, and Configure reassessment rules to set this plan's cadence.
A sensible starting cadence
A sensible starting cadence
- Critical: every 12 months
- High: every 24 months
- Medium: every 36 months
- Low: manual only
Step 8: Report and email templates
This step makes every output, whether an assessment readout or a vendor email, land in your organization’s format and voice. For report templates, go to Configuration → Assessment Settings and turn on Assessment report templates. Build a branded template using tokens (fields from the assessment and vendor record) plus custom AI prompts for freeform sections, like “give a meaningful analysis of the limitation of liability as it relates to their DPA.” If you do not have a house format yet, start from the Coverbase best-practice template with your branding.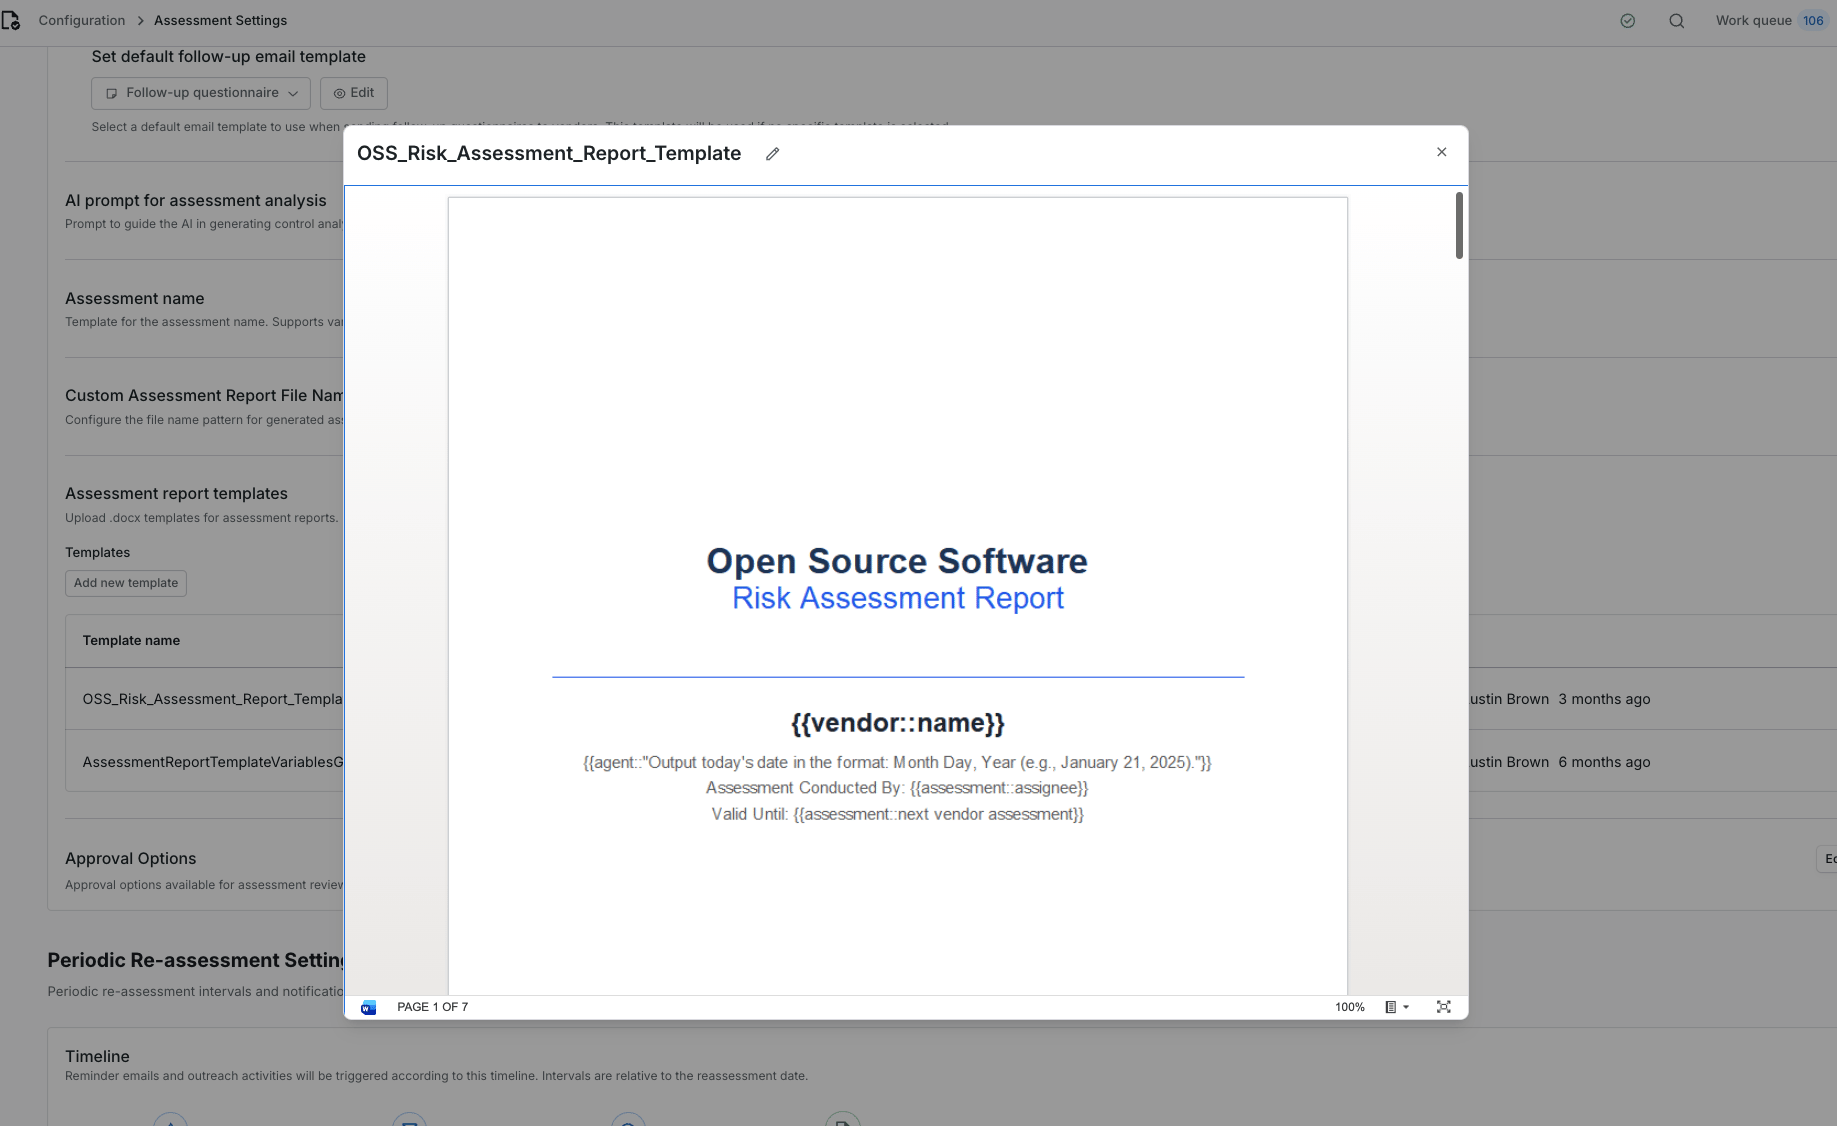
The report template builder. Tokens pull structured fields, and custom AI prompts fill freeform sections in your voice.
.docx will want the full reference open alongside it. Tokens are called placeholders in those pages.
Custom Word report templates
.docx: placeholder syntax, AI prompt sections, repeating findings tables, signature anchors, and what happens when a placeholder cannot be filled.Placeholder reference
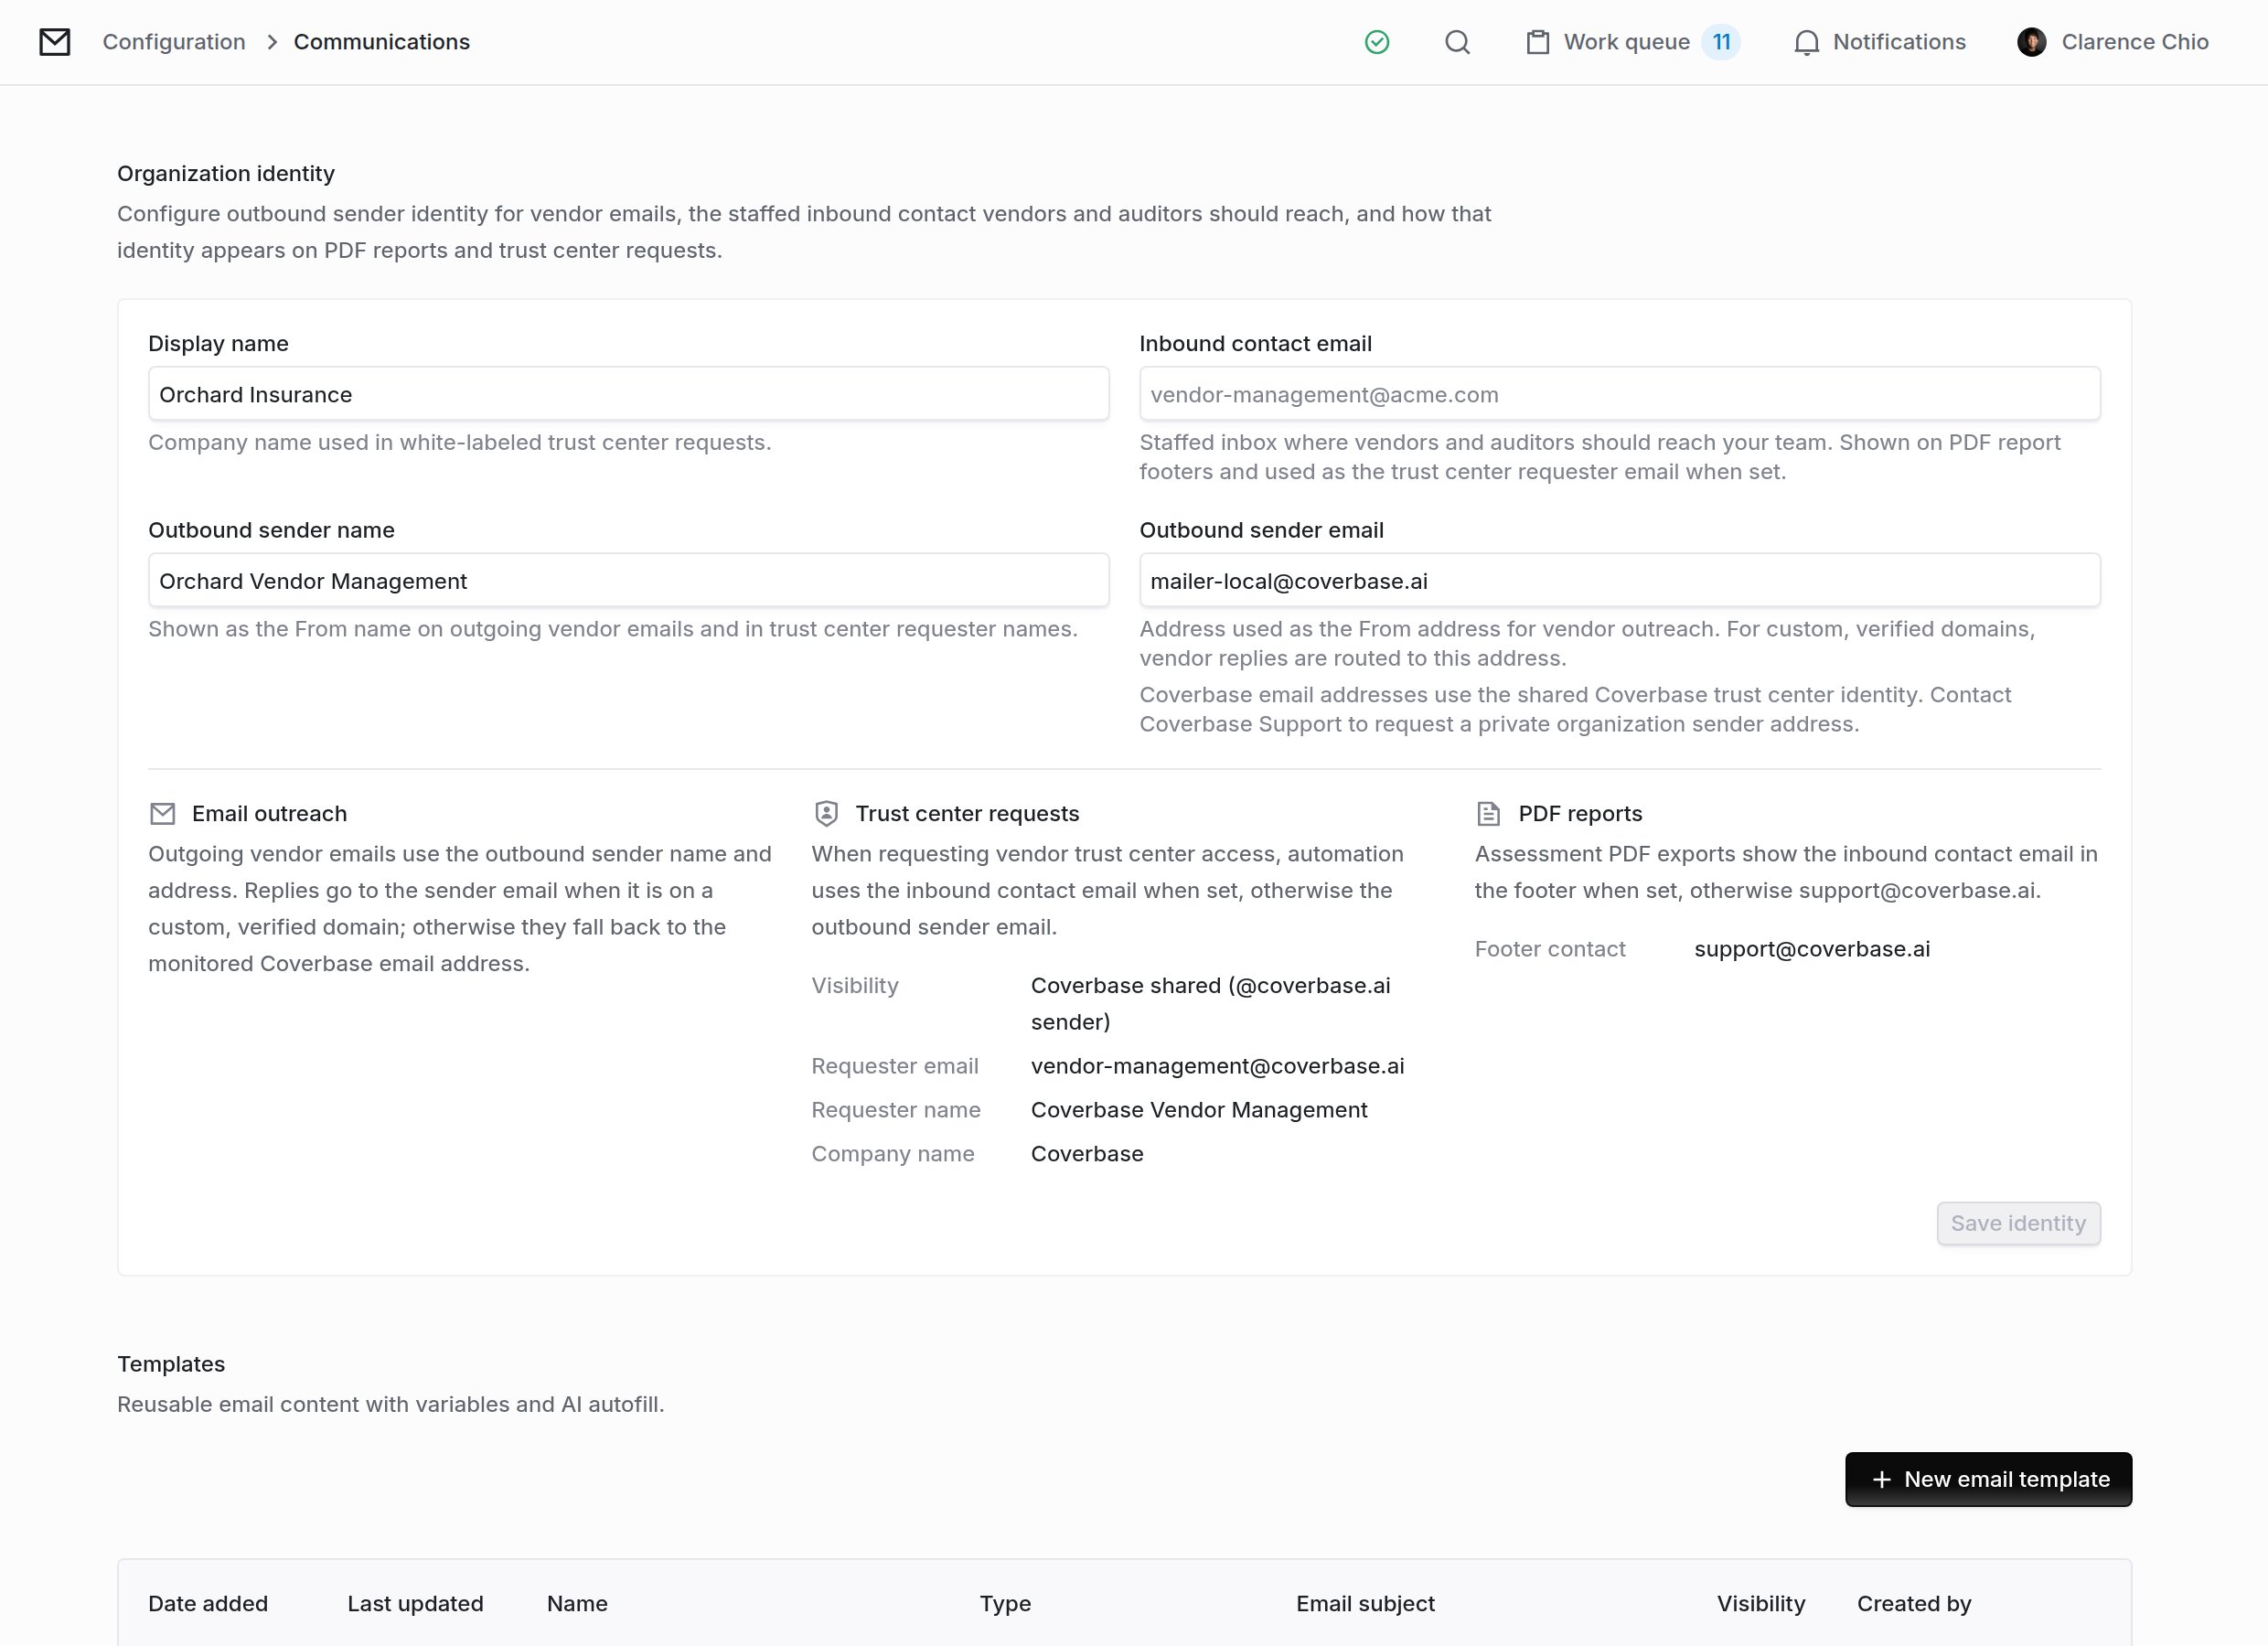
Configuration → Communications. Organization identity sets who vendor email comes from; the Templates list below holds the wording.
Step 9: Configure Radar (continuous monitoring)
Radar is the external intelligence layer. Sources feed detectors, and detectors fire on the events that matter, which reach your analysts as signals. Sources and detectors live under Configuration → Radar. The Configurations menu on the Radar page opens its Detectors, Sources and Reassessments tabs.- Review the out-of-the-box sources: SEC filings, CVE feeds, CISA advisories, and security and financial news, all pulled several times a day. Add any public RSS feed at no extra cost, or connect a ratings platform like Black Kite as an API source.
- Create detectors around what you act on, such as breaches and vulnerabilities, supply-chain disruption, or SEC and regulatory actions. Each detector takes plain-language guidance, example events to focus on, impacted risk domains, and a severity threshold. Switch on its risk impact, and set the point range, if acting on its signals should move residual risk (see risk propagation).
- Test each detector before you enable it, and start with tight severity thresholds.
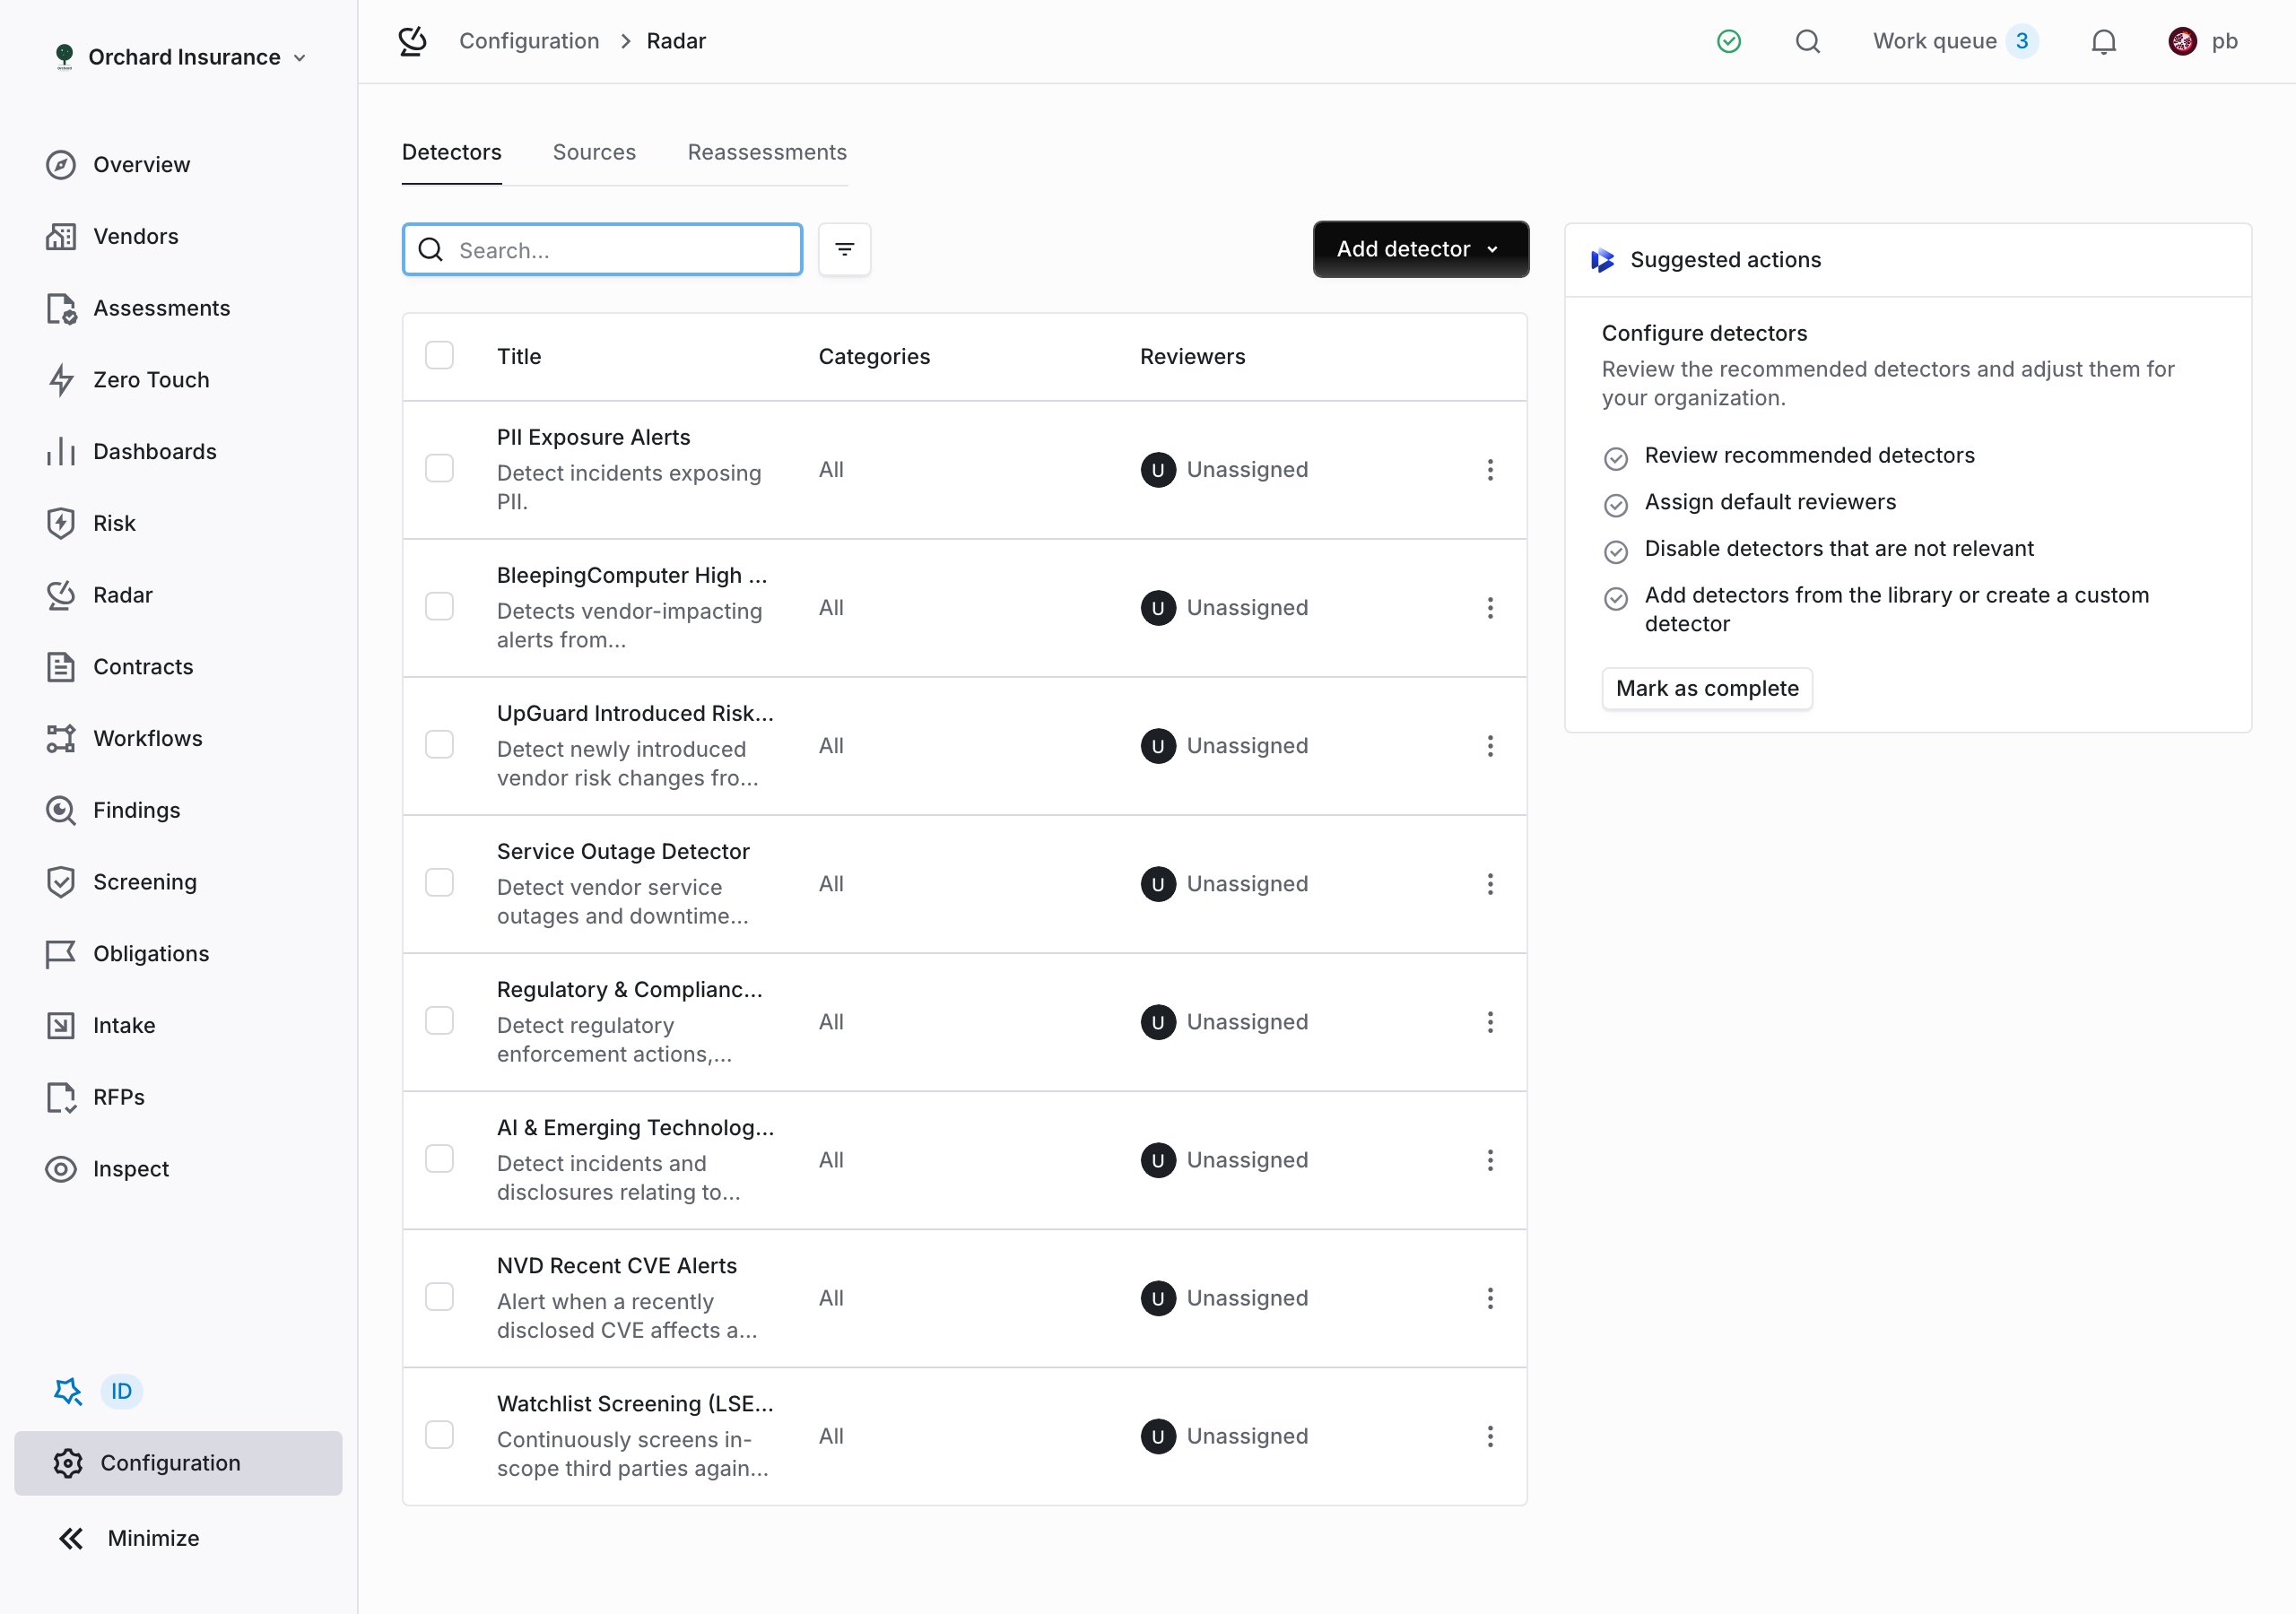
Radar detectors, under Configuration → Radar. Each one is scoped to what you will act on, with its categories and reviewers.
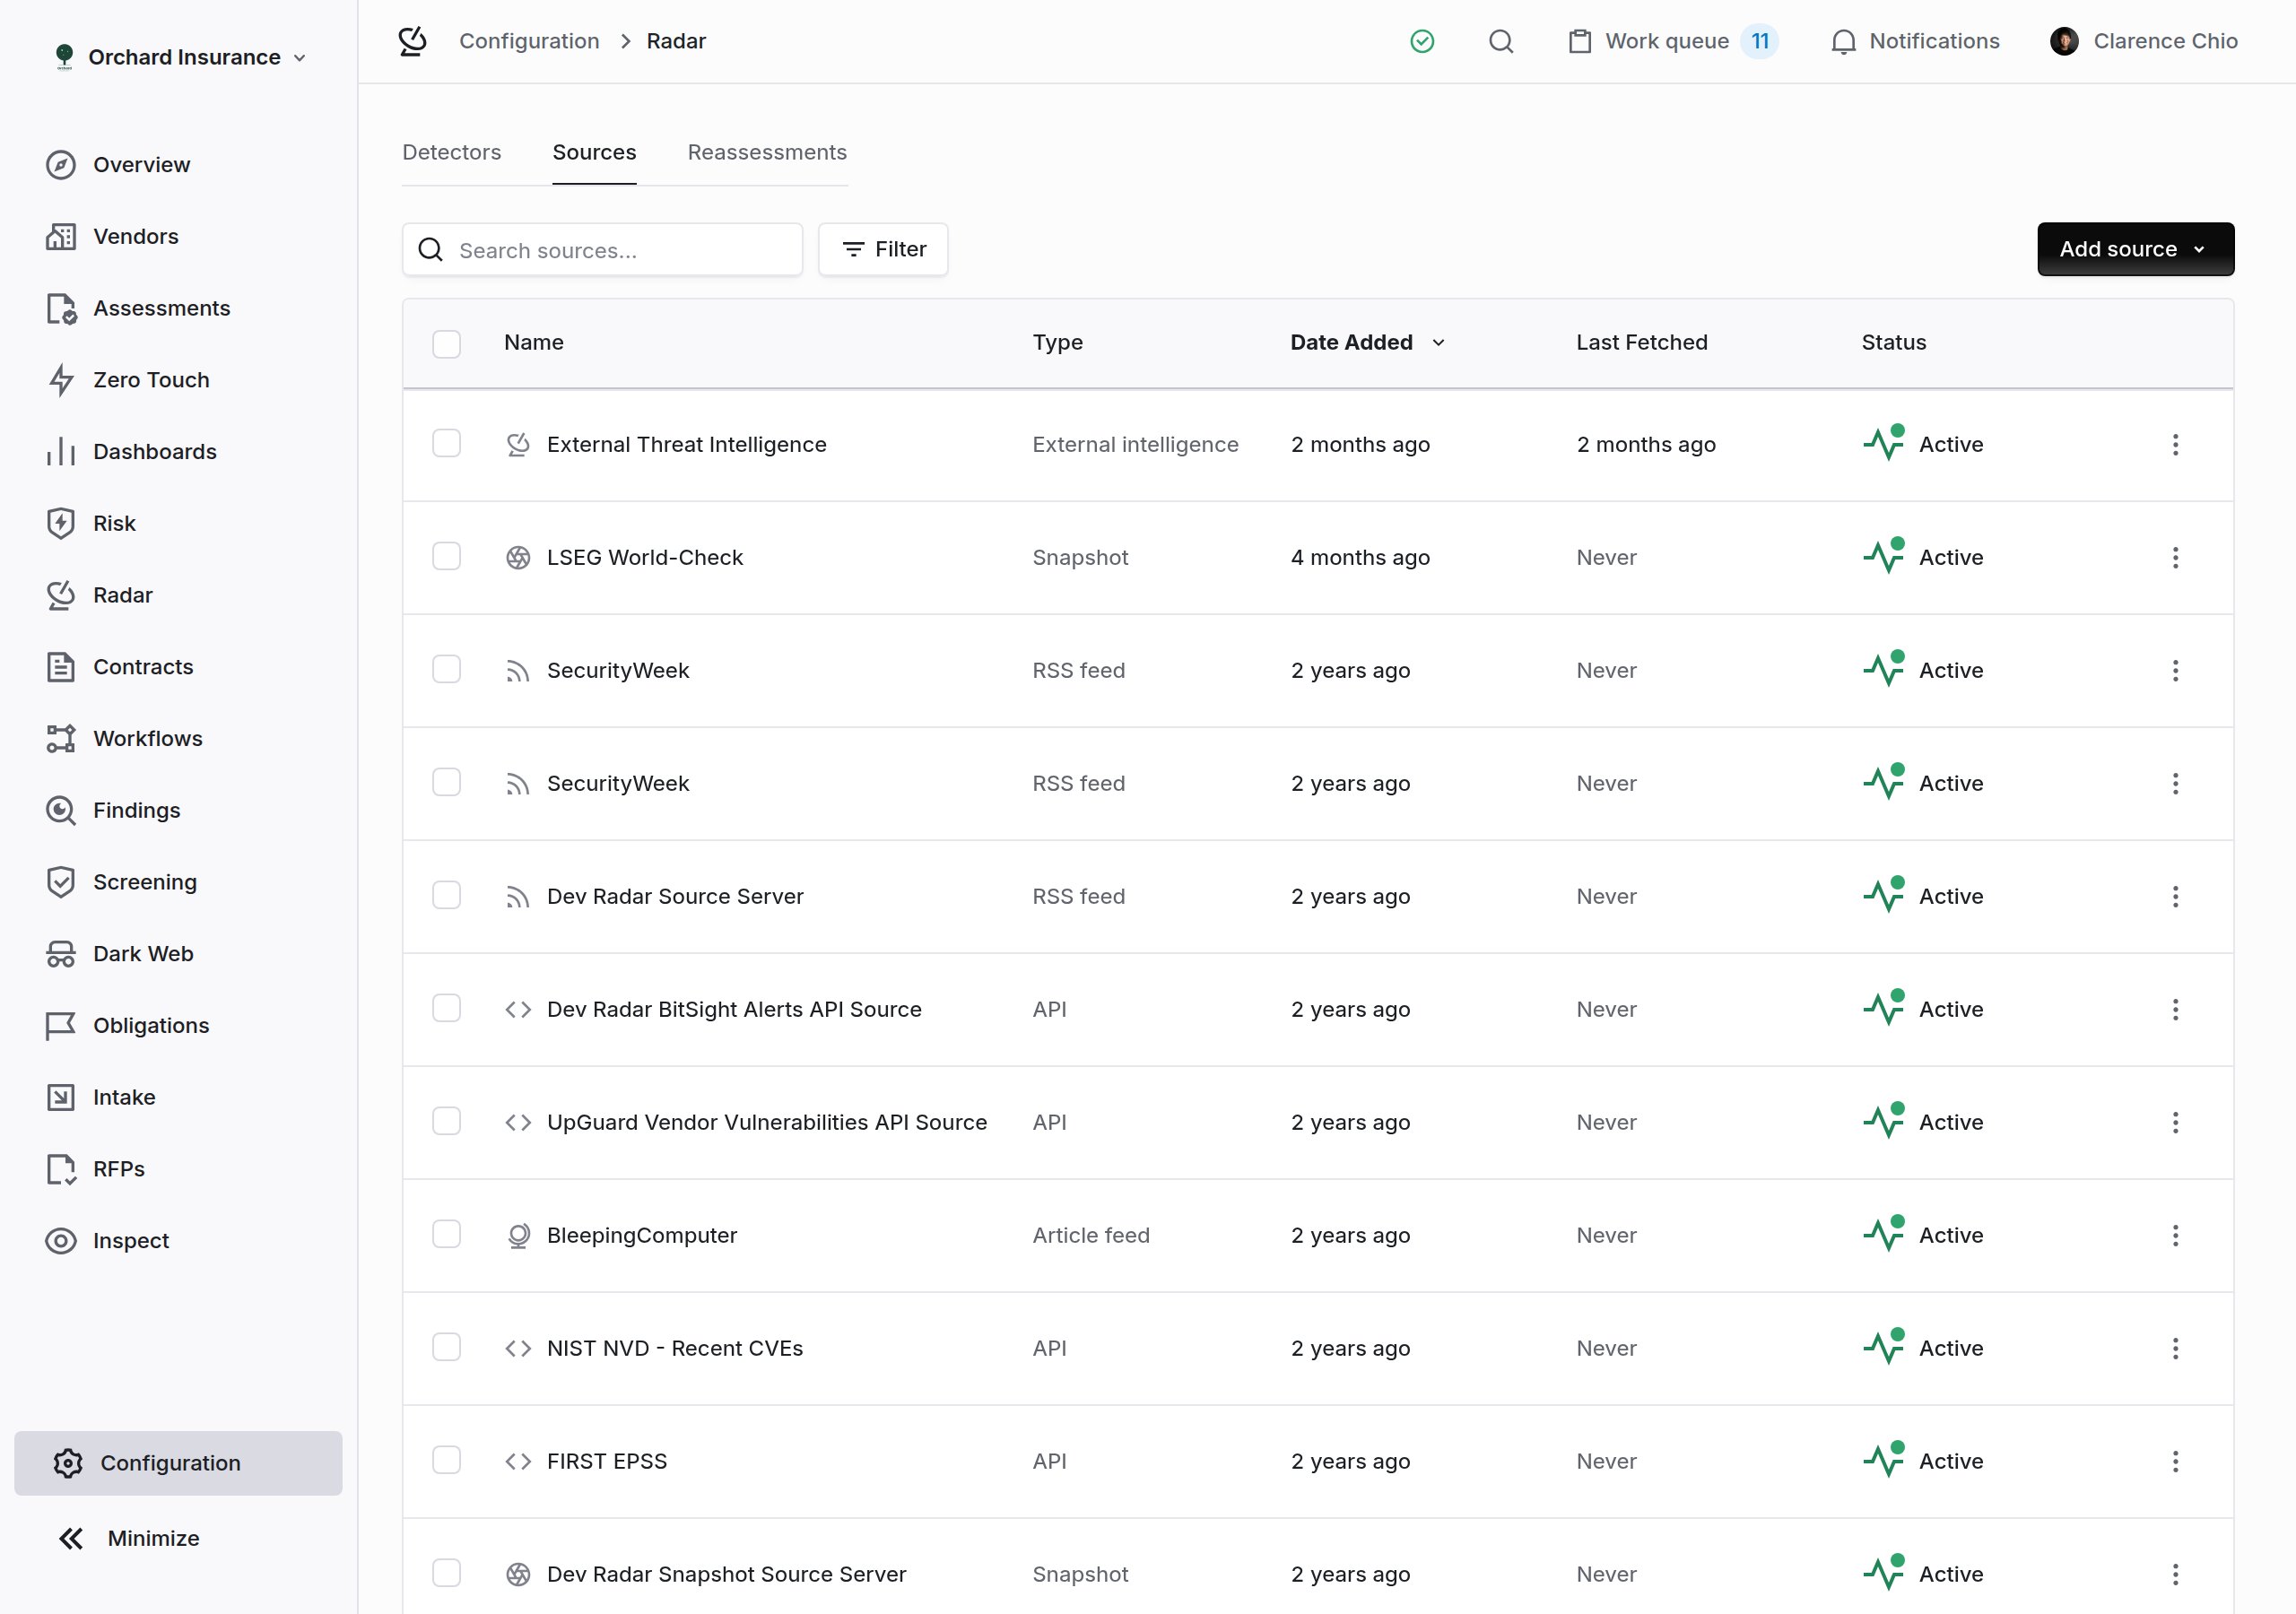
Radar sources, under Configuration → Radar. Built-in feeds plus any public RSS feed or connected ratings API.
Step 10: Enable obligations extraction
This step turns on extraction of what vendors require of you: CUECs from SOC reports (pulled verbatim) and shared responsibilities from contracts, DPAs, and terms.- Go to Configuration → Obligations and turn on Auto-create obligations from vendor CUECs (from SOC reports) and Auto-create obligations from contract shared responsibilities (from contracts).
- Re-trigger analysis on documents you uploaded before you enabled this. Extraction only runs on documents processed after the setting is on.
- Optionally, upload your internal control set so extracted obligations can be checked automatically against controls you already have in place. If a matched obligation should wait for a business unit to confirm it before it counts as satisfied, also turn on Require business-unit acknowledgement.
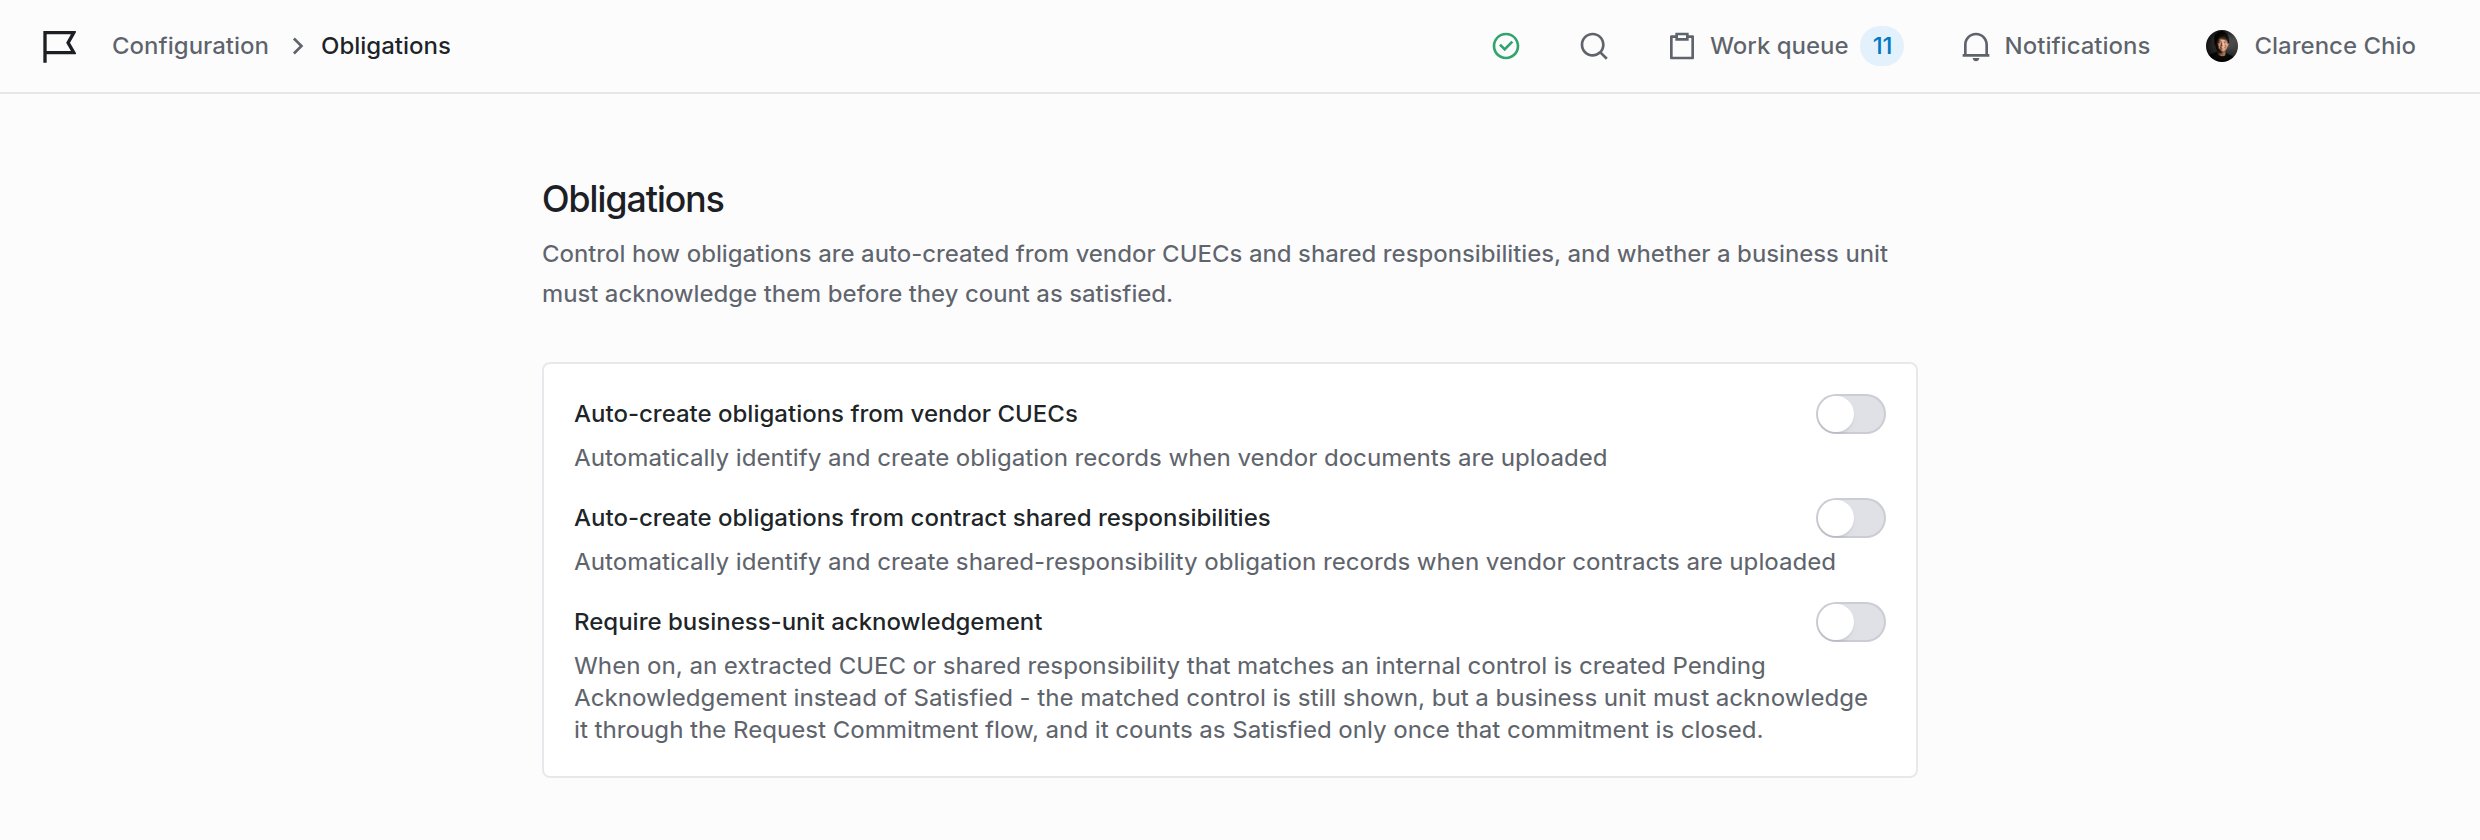
Configuration → Obligations. One switch each for CUECs and contract shared responsibilities, and one for business-unit acknowledgement.
Step 11: Integrations and Export API (optional)
This step exposes Coverbase data to external systems like GRC platforms, ticketing, and data warehouses.- Go to Configuration → Organization → API keys and choose Add new key. Name it, set an expiration, and store the bearer token securely: a key is shown once, when it is created.
- Go to Configuration → Coverbase API, stay on the Export API tab, and choose New Export Report. Pick the object the report returns and map which fields to expose. Note the GET endpoint shown on screen.
- For GRC integrations (findings out to your audit platform, controls back in), scope what needs to flow with your Coverbase contact, whether that is findings, residual-risk ratings, or control-environment scores.
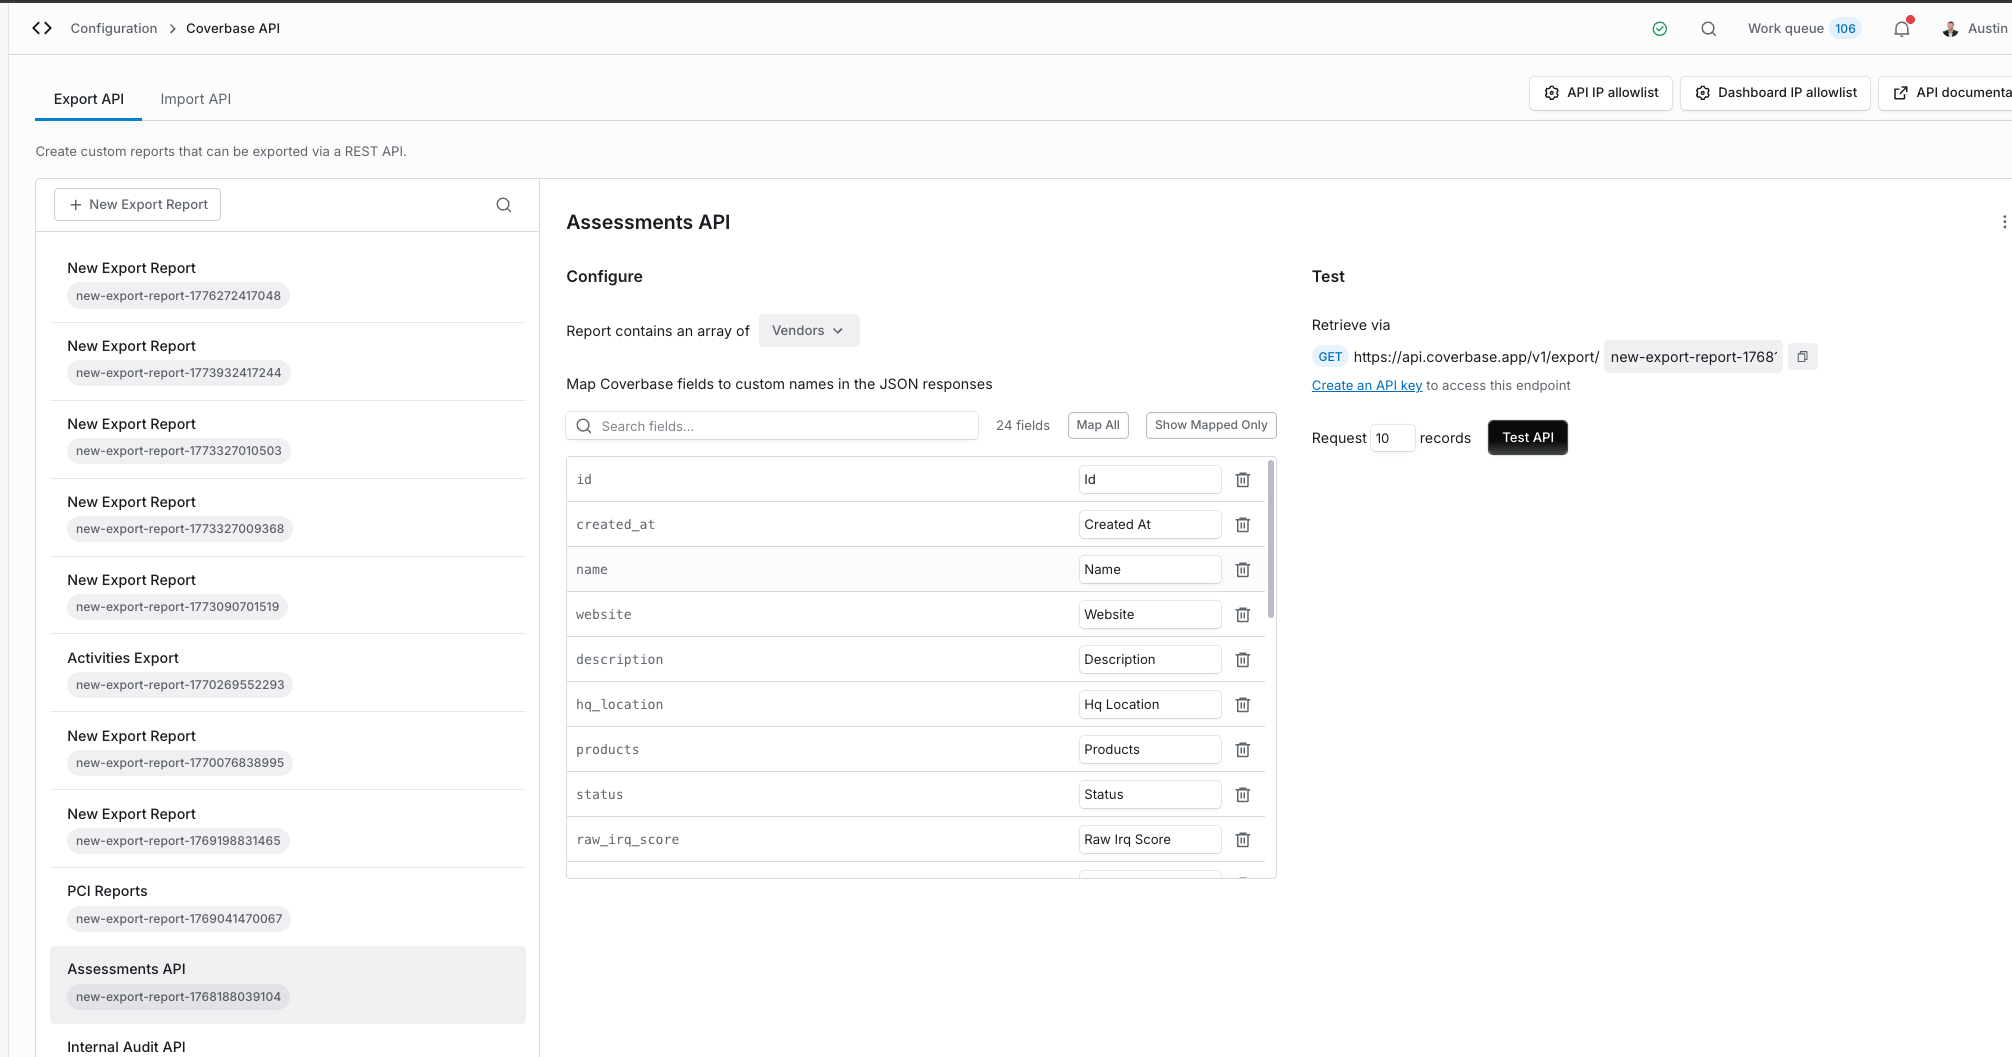
The Export API configuration. Map objects and fields, then read the source schema and GET endpoint right on screen.
Admin quick reference
Five rules:Changes are not retroactive
Weight before you launch
Tags drive everything
Required means blocking
Guidance beats strictness
Frequently asked questions
How long does initial setup take?
How long does initial setup take?
Do we need to configure all control frameworks at once?
Do we need to configure all control frameworks at once?
What if we don't have an existing IRQ?
What if we don't have an existing IRQ?
How does AI assessment work?
How does AI assessment work?
What if the AI makes a mistake?
What if the AI makes a mistake?